Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

MDR vs XDR: which do you need in 2026?

Quick definitionManaged detection and response (MDR) is a managed security service that provides human-led monitoring, investigation and agreed response actions through a remotely operated security operations center.Extended detection and response (XDR) is a technology platform that correlates security telemetry across multiple domains and provides investigation tools and automated response capabilities for security teams.

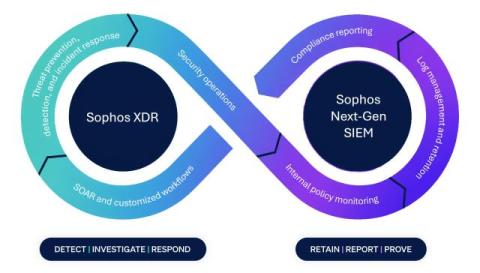
The industry turned XDR and SIEM into categories. Sophos turned them into outcomes.

Sophos Next-Gen SIEM, now generally available as part of Sophos Fusion, brings security operations and compliance together through shared context. For years, the cybersecurity industry has blurred the lines between XDR and SIEM. As capabilities converged, organizations were left trying to connect separate security operations and compliance solutions, often moving the same data between different tools, workflows, and teams.

What is managed XDR (MXDR)? A complete guide for service providers

Security teams rarely lack alerts. The harder problem is working out which ones belong to the same attack — and doing it quickly enough to stop the damage. An endpoint tool may flag suspicious activity on a device. An identity platform may record an unusual sign-in. An email security product may spot a malicious message. When those systems operate separately, each one shows only part of the incident.

Managed EDR and XDR services: how MDR delivers 24/7 protection for MSPs

EDR (endpoint detection and response) and XDR (extended detection and response) are technologies. MDR (managed detection and response) is the managed service that continuously operates them — the 24/7/365 SOC team that monitors, investigates and responds to threats on the client’s behalf, built on top of EDR, XDR, or another detection stack.

NGAV vs EDR vs XDR vs MDR: how to choose the right detection and response approach

NGAV (next-generation antivirus), EDR (endpoint detection and response), XDR (extended detection and response), and MDR (managed detection and response) are not four separate products bought independently — they are overlapping capabilities and delivery models. NGAV is a prevention capability, normally built into an endpoint protection platform or an EDR solution, that uses AI and behavioral analysis to block known and unknown threats.

Unified ITOps + Security Platforms: 10 Tools Closing the Gap

Most MSPs run IT operations and security on two separate stacks. That means two consoles, two data sets, and one endpoint that both teams fight over. The 2026 buying shift is toward a single platform that does both, and the vendor landscape has reorganized around it.

5 Must-Have Factors to Look for in an XDR Security Solution

With the rise of data breaches and hacking attempts, a strong cybersecurity posture is the most significant need today. Given the scale of cybercrime growth, you need to carefully consider several key factors that will ultimately impact the cybersecurity solution you pick. Businesses have realized the value of their data; now they must invest in tools to easily detect and respond to security issues.

Should Your Organization Rely on XDR For Cybersecurity?

The cybersecurity industry’s evolution from perimeter protection to holistic visibility, detection, and response is perhaps best illustrated in the evolution from endpoint protection platforms (EPP) to comprehensive security solutions that provide holistic protection for an organization’s ever-expanding attack surface, including network, cloud, and identity. Extended detection and response (XDR) is one of those solutions.