Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Building a bot takes five minutes. What it stands on took eight years. Introducing LimaCharlie Bots.

Co-founder and CCO We shipped bots in the LimaCharlie AI Terminal. You can create one in a few minutes: give it a role, pick a profile if you want one, and open a chat. I said this during our September Build Log demo and I'll repeat it here, because everything else in this post follows from it. The bot is the easy part.
PoSA v1.11: Turning Fragmented Attack Signals Into Actionable Risk

With PoSA v1.11, we focused on a practical problem: detecting more attack activity does not necessarily help fraud and security teams make better decisions. PoSA already identifies activity across digital impersonation, credential theft, attacker devices and account access. The challenge is making the connections between that activity easier to understand, identifying which users and devices require attention, and making that intelligence available to the systems and teams responsible for responding.

Introducing The GitGuardian Mixin Kit To Extend Docker Sandboxes for Safer AI Coding

Modern enterprise security is increasingly being tasked with keeping agents from affecting critical data and infrastructure. In this video, Dwayne, principal developer at GitGuardian, introduces how GitGuardian AI hooks extend the power of Docker Sandbox isolation. Their micoVM architecture plus the power of ggshield mean anyone can get an agent working in a secure way with very little effort. Chapters.

What's New at GitGuardian: AI Leak Triage & Laptop Secrets Scanning

We found 15x more valid secrets on developer laptops than in code repositories. In this September edition of What's New in GitGuardian, Sr. Product Managers Léna Cuissard and Emmanuelle Franquelin walk through two updates: agents that triage public secret leaks for you, and Developer Endpoint Protection coming together as one package.

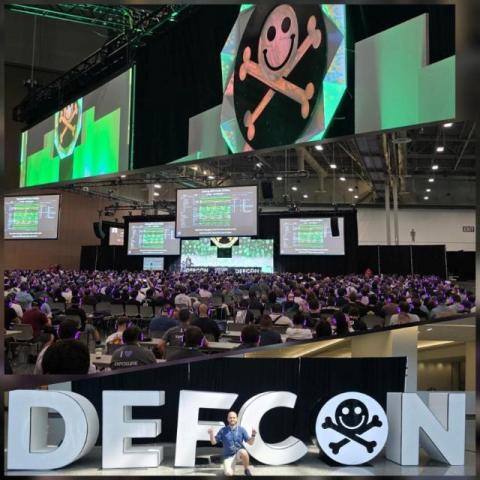
DEF CON 34: Lessons Beyond the Conference

Being part of the cybersecurity community means more than simply following the news or reading security research. It is about getting involved, having conversations, sharing experiences, discussing problems, and learning from peers who face similar operational challenges. Of course, all of this comes with an investment of time, energy, and a full day of travel to reach one of the world’s largest hacking conferences: DEF CON in Las Vegas.

Singapore & MAS AI Red Teaming Requirement: A Closer Look

Security leaders at key financial institutions in Singapore now have a new line in their compliance calendars: AI-assisted red teaming, a requirement MAS introduced on 1 July 2026. What appears to be a scoping exercise actually asks a harder question, i. e., how does a bank differentiate between another convincing report and one that secures the institution?

Zero-Day Attack Prevention: Catching Unknown Vulnerabilities Before Threat Actors Do

On September 1, 2026, OpenAI announced that its Astra model had reached the Critical tier for cyber capability under the company’s Preparedness Framework, a first for its systems. While working through an internal benchmark of 20 recently disclosed vulnerabilities in Google’s V8 engine, the model found two zero-days that no one had asked it to look for and used them in a working exploit chain. OpenAI is disclosing both flaws and restricting the capability to vetted testers.