Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why the Biggest Breaches Still Come Down to the Basics | Nicole Perlroth at Black Hat

At Black Hat last year, Garrett Hamilton asked Nicole Perlroth what she wanted the next five years of security to look like. She didn't give the optimistic answer. She said she was genuinely terrified. Zero-day exploitation at scale, fully automated. Attackers turning AI into infrastructure of their own. A year isn't five. But it's enough to check the tape.
Offense Is Running on AI. Is Your Defense? | AI, Configuration Drift & Prevention

Offense is running on AI. Defense has to as well. That's the throughline of Garrett Hamilton's conversation with Jay Wilson, CIO and CISO at Insurity, on The Security Strategist, hosted by Shubhangi Dua at EM360Tech. What they get into.

How AI Is Changing What Security Teams Can Actually Do | Nancy Phillips, Ensemble Health Partners

Threat actors used to need days or weeks to exploit a vulnerability. Now AI lets them do it in seconds. Most security teams are already buried. Too many tools, too many alerts, manual processes that can't keep pace, and break-glass changes that get made and forgotten. Keeping everything configured and optimized correctly is a full-time job on its own. Nancy Phillips, Chief Information Security Officer at Ensemble Health Partners: "I want my teams doing the innovative stuff. Not the mundane, repeatable stuff.".

Exposure Management Explained: How to Go Beyond Vulnerability Scanning

Vulnerability scanning gives security teams a starting point, but it has never been the whole picture. Scan results capture known CVEs across applications and systems, yet they say nothing about whether a given weakness is actually reachable, whether the controls around it are functioning correctly, or whether the people with access to it represent a meaningful risk. Exposure management addresses all of that.

Misconfigured Security Controls Open the Door for Storm-2949

The Microsoft Defender Security Research Team and Microsoft Threat Intelligence documented a campaign in which Storm-2949 abused Microsoft Entra ID accounts to exfiltrate data from Microsoft 365 and Azure environments. The attack shows how cloud intrusions increasingly unfold through identity systems, administrative features, and legitimate platform capabilities rather than obvious malware or traditional endpoint compromise.

Kevin Mandia on AI-Powered Attacks: The Race Just Got Faster | Black Hat | Reach Security

At Black Hat last year, we sat down with Kevin Mandia to talk about what's coming. His take: offense is going to accelerate with AI. Not slow down. Not plateau. Accelerate. When you've run more red teams than practically anyone on the planet, the pattern is clear. Getting into a victim network is already a race. AI compresses those time frames further. The attack surface isn't changing. Misconfigurations, things that slipped, controls that were on and got turned off. The entry point stays the same. AI just makes the race to exploit it faster.

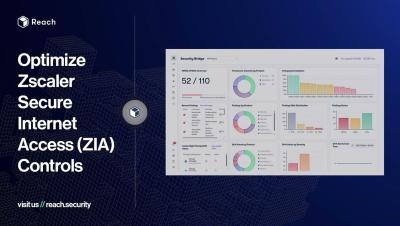
Optimize Zscaler Secure Internet Access (ZIA) Controls | Demo Video

Zscaler Secure Internet Access (ZIA) provides powerful secure access, inline inspection, decryption, and data loss prevention capabilities. But as your security and IT environments scale, and security controls change, Zscaler ZIA protections can drift away from established baselines, increasing your risk and leaving you open to attack. Reach analyzes your Zscaler ZIA controls to find and fix misconfigured controls, activate unused capabilities, and stop configuration drift. This hardens your defenses and protects you against fast-moving adversaries.

Close Defensive Gaps Before AI Attacks Exploit Them

The speed of AI-powered attacks is mind-numbing. CrowdStrike found that average eCrime breakout time fell to 29 minutes, with the fastest recorded breakout at 27 seconds. Armadin showed an LLM-driven NTLM relay attack completing in under three minutes, then roughly 1.5 minutes with BloodHound MCP context.

Security Hardening Explained: Why is it Critical for Your Security Program?

Security hardening is the practice of systematically reducing the ways an attacker can get into, move through, or persist in your environment.The reason this is a priority is that the gap between "deployed" and "properly configured" is where most breaches actually live. This guide covers the core principles of hardening, how it maps to compliance requirements, and how automated tooling has changed the way mature security teams operationalize it at scale.