Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

Could PHP2Shell pose a cybersecurity risk on the scale of Log4j? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. With millions of potentially affected systems and limited patching options for legacy PHP versions, security teams face a complex remediation challenge.
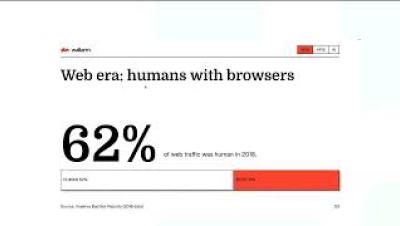
Agentic Operators for Web Application and API Protection

The days of vendors selling naked tools that drive up professional services revenue are coming to a close. AI is making it possible to not just automate human tasks, but to deliver an entirely new agent operator-based platform. Humans become managers of agentic operators, and the operators do the day-to-day work of securing web applications and APIs.

Sophos Network Security: Use Network Maps

Network Map helps admins quickly visualize network topology, understand device relationships, and troubleshoot connectivity issues from a single interface. Learn how to access and use Network Maps in Sophos Fusion to locate devices, utilize Live Discover queries to retrieve device history, and block or release hosts with Active Threat Response (ATR) powered by Sophos Fusion APIs. Ask questions and get expert answers in the Sophos Community.

New Prompt Injection Techniques Cover Agent-Planning Attacks

Prompt injection started as a simple idea during its initial chatbot phase: Tell the model to ignore its instructions and return information in violation of its guardrails. Now, prompt injection attacks can aim at something harder to see: how an agent plans, and how a model reasons and decides which rules apply.

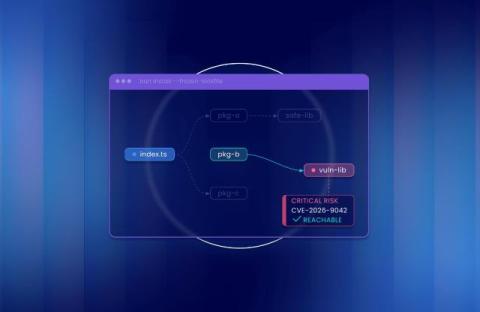
Mend SCA now supports Bun, with reachability built in

TL;DR: Mend SCA now scans Bun-managed JavaScript and TypeScript projects, including both the text-based bun.lock and legacy binary bun.lockb lockfiles. It detects direct and transitive dependencies automatically, works in the Mend CLI and every repository integration, and supports reachability analysis so teams can fix the vulnerabilities their code actually calls first.

Securing the Future of AI

How Kroll and CrowdStrike Are Turning Innovation into Value for Customers At Fal.Con 2026 in Las Vegas, Kroll Managing Director Robb Mayeski joined CrowdStrike Vice President of Global Scale Partnerships Dan Danielli for a live interview with theCUBE, SiliconANGLE. The discussion explores how Kroll and CrowdStrike are helping organizations defend against AI-accelerated threats while adopting AI in a way that delivers measurable business value and strengthens cyber resilience.

Forward Threat Exposure: Know What an Attacker Can Reach

Cybersecurity is reaching an inflection point. Attackers use AI to research vulnerabilities, develop exploits, and run increasingly automated campaigns, compressing the time defenders have to respond. As that window shrinks, defenders need to know which vulnerabilities an attacker can actually reach. Answering that question is difficult when security tools provide separate views of vulnerabilities, assets, and network controls.

Business IT Support: Should You Outsource or Keep It In-House?

For most small businesses, outsourcing business IT support gives more cover for less money than hiring your own IT person. Some firms prefer to keep IT in-house for direct control, and many larger ones combine their own team with a provider, an approach called co-managed IT. The choice affects more than your IT bill. It decides who spots problems and fixes them, and whether your IT knowledge stays with the business when someone leaves.