Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

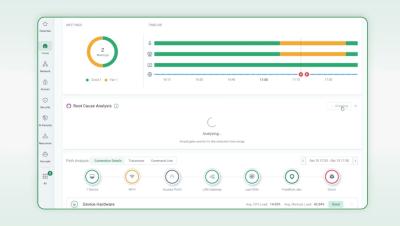
Cato DEM Root Cause Analysis: Find What's Slowing Down Your Applications

When users report slow application performance, where do you start troubleshooting? The Wi-Fi, ISP, network, or application itself? With Cato Digital Experience Monitoring (DEM), IT teams can move beyond guesswork and identify the root cause of performance issues using evidence from across the user-to-application path. In this demo, a user reports slow Zoom performance at a branch location. Watch how Cato DEM Root Cause Analysis investigates the issue, examines latency, jitter, and packet loss, and identifies the branch wireless LAN as the source of the slowdown. See how Cato DEM helps IT teams.
Beyond Deployment: Evaluating the Operational Impact of an SD-WAN Refresh

Many SD-WAN refreshes start with an expiring contract or edge equipment reaching end of life. But replacing the edge should not be the measure of success. For network and infrastructure leaders, the real test is what improves after the refresh. Will the refresh put IT on another appliance cycle, or move the WAN to a cloud service? Can IT keep critical applications performing consistently? Can the WAN respond when network conditions change?

Why AI Red Teaming Belongs at the Core of Your AI Security Program

Enterprises are putting AI applications and agents to work on sensitive data and business workflows, while attackers look for new ways to manipulate the models and exploit the tools connected to them. Security leaders need to know whether those systems will hold up against a real attack, and AI red teaming gives them that answer by testing AI the way an attacker would.

Cato AI Red Teaming: Find AI Model Risks Before Attackers Do

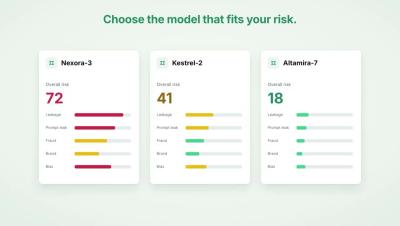
AI-powered applications depend on the models behind them, and those models keep changing. New attack techniques appear every day, model updates can change how safeguards behave, and switching models can leave existing protections behind. Security teams need to know where their AI is exposed before an attacker finds out first.

Stopping destructive commands in AI agents

An engineer gives a coding agent a routine task: clean up an old test deployment. The request sounds harmless, and the environment is cluttered with unused cloud resources, stale branches, and temporary credentials that should have been removed weeks ago. The agent gets to work. It lists resources, identifies old infrastructure, and finds a deployment command. Then it sees a naming pattern that appears to connect the test environment to production.

Wait, Did We Just Invent Classifiers Again? Introducing Jev, a new way to do AI.

For the last few years, when somebody says “AI,” what they are usually referring to is a Large Language Model, or LLM for short. You chuck some text in, it has a think, and it gives you some more text back. This is brilliant if you want code written, documents summarised, or quantum physics explained to you in a limerick, but while this is great for humans, most software doesn’t actually want a beautifully written paragraph. Software just wants an answer so it can make a decision.

Beyond Model Access: Frontier AI Defense Needs Runtime Prevention

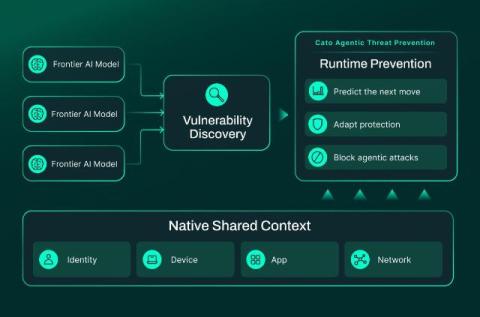
Access to powerful AI models is opening new possibilities for cybersecurity. Models can help uncover weaknesses, investigate threats, and explore how attackers might break into an environment. Using several models can bring different strengths to that work. But model access alone does not answer a critical question: can your defense stop an attack while it is happening? In the frontier AI era, discovery needs to connect to action.

Securing what your Bedrock AgentCore agents actually do

An AI agent is software that can act on your behalf. It may read documents, emails, and web pages, then use the systems you connected to complete a task. Amazon Bedrock AgentCore makes these agents faster to build and deploy. But securing them requires more than limiting which systems an agent can access. You also need to consider what the agent can read once it gets there. A document, email, or web page may contain hidden or malicious instructions designed to influence an agent’s next action.

When the Enterprise Edge Is Everywhere, Security Must Be Too

With hybrid work as the new standard, consistently enforcing security across every edge is a challenge for teams. Working from any location or device creates a persistent challenge: how to enforce consistent, risk-based access controls across users, devices, and applications without introducing policy gaps or operational complexity. To understand the impact, let’s consider the user experience within a single global organization operating across three continents.