Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Emerging Threat: (CVE-2026-89110) SAP NetWeaver Visual Composer Broken Access Control

CVE-2026-89110 is a broken access control vulnerability in SAP NetWeaver Visual Composer, classified as CWE-749, Exposed Dangerous Method or Function. Certain portal functionality does not perform sufficient authorization checks, and a low-privileged attacker can use it to invoke internal operations on a preconfigured remote system. The vulnerability carries a CVSS v3.1 base score of 9.9 (Critical), with the vector AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H.
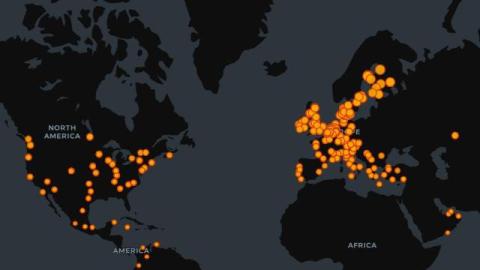
The Quiet Takeover: How Your Forgotten Cloud Resources End Up Selling Slot Machines

Picture a global telecom company. Three years ago, a marketing team launched a campaign microsite on a cloud platform and pointed a company hostname at it. The campaign ended and the team deleted the app. Nobody deleted the DNS record. A few years ago, that mistake could sit there for a decade. No one was looking. Today, attackers run automated sweeps across millions of domains, resolving every DNS record and checking whether the resource behind it still exists.

Emerging Threat: (CVE-2026-107406) NetScaler ADC and Gateway Remote Code Execution via SAML

CVE-2026-107406 is a memory overflow vulnerability in NetScaler ADC and NetScaler Gateway, classified as CWE-119. Successful exploitation leads to remote code execution or denial of service. The vulnerability carries a CVSS v4.0 base score of 9.5 (Critical). Attack vector is network, and neither privileges nor user interaction are required.

Emerging Threat: (CVE-2026-21589) Atlassian Data Center Arbitrary File Access via Path Traversal

CVE-2026-21589 is an arbitrary file access flaw affecting most of Atlassian’s self-hosted Data Center product line. CISA classifies it as CWE-552, files or directories accessible to external parties. An unauthenticated remote attacker can read specific files inside the web application root directory. The vulnerability carries a CVSS v4.0 base score of 9.3 (Critical). Attack vector is network, attack complexity is low, and neither privileges nor user interaction are required.

Emerging Threat: (CVE-2026-94483) Next.js Server-Side Request Forgery via Image Optimization

CVE-2026-94483 is a server-side request forgery flaw in the Image Optimization feature of Next.js, the React framework maintained by Vercel. It is classified as CWE-918. Image Optimization fetches a remote image on the server and re-encodes it. Before fetching, it checks the requested URL against the images.remotePatterns allow-list. The flaw is that the allow-list check and the fetch resolve DNS separately, so a host that passes the check can resolve to a different address by the time the fetch happens.

Emerging Threat: (CVE-2026-84411) MikroTik RouterOS Unauthenticated Root RCE via Web Management

CVE-2026-84411 is an integer underflow in the web management service of MikroTik RouterOS, classified as CWE-191. The flaw sits in the service’s HTTP request body handling and is reachable before authentication. A single crafted request lets an unauthenticated network attacker execute arbitrary code as root, or crash the device. The vulnerability carries a CVSS v3.1 base score of 9.8 (Critical) and a CVSS v4.0 base score of 9.3 (Critical).

Emerging Threat: (CVE-2026-86858) ServiceNow AI Platform Unauthenticated Privilege Escalation via GraphQL

CVE-2026-86858 is an improper access control flaw in the ServiceNow AI Platform, classified as CWE-284. ServiceNow describes it as an unauthenticated privilege escalation reachable through GraphQL. In certain circumstances an unauthenticated user can create, modify, or delete instance data beyond what was intended. The vulnerability carries a CVSS v4.0 base score of 8.7 (High). Attack vector is network, attack complexity is low, and neither privileges nor user interaction are required.

Attack Surface Management Vendors Compared

Most attack surface management (ASM) evaluations start with a name already on the table: a vendor from a G2 grid, an analyst shortlist, an inbound email, or a renewal conversation. Before you commit to a proof of concept (POC), you need to know how it compares. This page provides a capability matrix across 10 ASM vendors, followed by an honest section on each. UpGuard makes one of the platforms on this list, so every section, ours included, covers where the product isn't the right fit.

Emerging Threat: (CVE-2026-94545) Next.js Remote Code Execution via ImageResponse SVG Injection

CVE-2026-94545 is a remote code execution vulnerability in the next/og ImageResponse API of Next.js, the React framework maintained by Vercel. ImageResponse generates images on the server, typically Open Graph preview cards, by rendering markup through the Satori library into SVG and then into a raster image.

Emerging Threat: (CVE-2026-69197) Umbraco CMS Protected Content Disclosure via Delivery API Expansion

CVE-2026-69197 is an authorization flaw in the Content Delivery API of Umbraco CMS, an open source ASP.NET content management system. The Delivery API enforces member and Public Access checks on the node a caller directly requests, but it does not apply those same checks to nodes referenced through Content Picker or Multi-Node Tree Picker properties. The gap extends to pickers nested inside Block List, Block Grid, and Rich Text Editor blocks.