Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Compute Just Became an Endpoint Problem

For the last three years, enterprise AI happened somewhere else. Models trained in someone’s cloud, inference ran behind an API, and the endpoint stayed where it had always been: on a laptop that opened a browser. With local AI computing platforms like NVIDIA DGX Spark (opens in a new tab), RTX Spark (opens in a new tab), and DGX Station (opens in a new tab), that framework is ending.

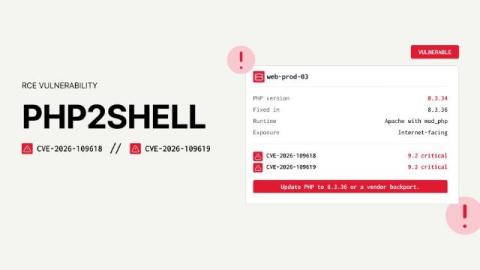
PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619

If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed this week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part.

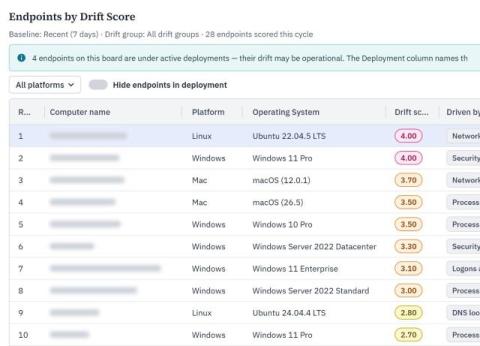
Notice when a machine stops acting like itself: introducing Endpoint Drift

The next attacker in your environment probably won't look like an attacker. With AI in the mix, they can sign in with stolen credentials and use the same tools your IT team uses every day. Nothing about that activity matches a known-bad file or a known-bad rule. That is the problem Endpoint Drift is built to solve. It learns what normal looks like for each endpoint, then shows you which ones have started behaving differently, and why.

Hunt or be Hunted: Every service was unique, and that was the problem

Stacking is usually the first thing we reach for on a persistence hunt. Pull every service, autorun or scheduled task across the environment, count how many endpoints have each one, and sort ascending. The entries at the bottom, the ones that show up on one or two machines, are where you start digging. In one Tanium Customer's environment, that didn't work at all. Each endpoint returned somewhere between a hundred and five hundred rows, and almost every one of them was unique to that endpoint.

Zero Touch Patch Automation: Tanium Tech Talks #172

How do you patch faster - all while honoring your patching policies and *not* breaking things? Attackers are using AI to find and exploit vulnerabilities faster, and vendors are shipping patches faster too. Your patching processes need to keep up! In this episode we show how to automate patching on a monthly cadence, roll it out in rings, and keep control of the process the whole way through. zero-touch, ring-based patch automation with Tanium deployment plans, in Atlas or the classic console.

Build the Self-Driving SOC with Tanium Security Operations

Attackers don't wait for humans, and neither should your SOC. Tanium Security Operations brings detection, investigation, hunting, and response together on one platform that moves at machine speed. See how Tanium Atlas works as an extension of your team: pulling live telemetry, historical activity, and the full process tree the moment a threat surfaces, hunting a hypothesis across every endpoint in your fleet, and containing threats from one endpoint to hundreds of thousands. When the hunt needs to go deeper, HuntIQ's hands-on experts take it from there, inside your environment.

AI is Accelerating Your Environment. Our Connector Keeps Up: The Next Evolution of the Service Graph Connector for Tanium & ServiceNow

The Service Graph Connector for Tanium has been a reliable and proven way ServiceNow customers keep their CMDB populated with Tanium endpoint data. As environments have grown and AI has accelerated the pace of change, the opportunity became clear: what if the CMDB could reflect that change as it happens, instead of catching up on a schedule?

Tanium Provision, "Bare Metal in 2026": Tanium Tech Talks #171

Tanium Provision takes a device from bare metal to domain-joined and software-ready, hands-off, from start to finish. This episode walks through the entire process, end to end. Rob Broughall takes us through the full provisioning journey: setting up the infrastructure, building a Windows 11 bundle from the ground up, and watching a device go from bare metal to domain-joined and running software in under two hours.