Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Bringing Tanium's real-time endpoint intelligence into enterprise AI workflows with MCP

Enterprise AI is quickly moving from experimentation to day-to-day operational use. Security analysts, IT operators, and platform teams are increasingly working inside AI-native environments — from Claude and Microsoft Copilot experiences to internally built agents and automation workflows. But there is a practical challenge: AI workflows are only as useful as the enterprise systems they can safely reach.

Introducing Agentic SecOps: Live Endpoint Truth for the AI-Driven SOC

Security operations teams are being asked to move faster than ever. Adversaries are using automation, infrastructure changes by the minute, and the number of alerts, exposures, and investigative paths keeps growing. But too many SOC workflows still depend on scarce expert time. A senior analyst writes the query, translates the hypothesis, pivots across tools, validates the result, and then hands the finding off for action. The craft works.

Tanium and Google Threat Intelligence bring Google-grade threat intel to the live endpoint

Security teams are under pressure to move faster, investigate more confidently, and make better decisions with fewer resources. But even the best security operations teams run into the same problem. They often do not have a reliable place to start. Threat hunting depends on high-quality intelligence and experienced analysts who know how to turn that intelligence into useful pivots. Alert triage depends on knowing which signals matter and which ones are noise.

Streamline Exposure Management Responses with Atlas

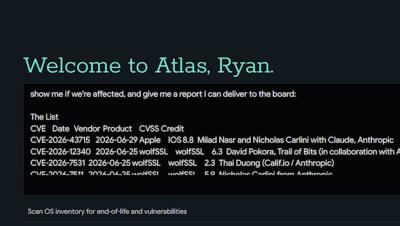
When 115+ new CVEs are released — Firefox, OpenSSL, WolfSSL, and more — figuring out your exposure used to mean hours of manual work: querying the CMDB, pulling reports, chasing tickets. In this video, we show a faster way with Tanium Atlas. We paste in the full list of CVEs and ask one question: are we affected, and can we get a report ready for the board? In under a minute, Atlas returns a full exposure report across thousands of endpoints, prioritized by what needs attention first. A follow-up question generates a remediation plan. The result.