Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Soteria scaled its MDR practice on LimaCharlie

Soteria started as a consulting and advisory firm focused on penetration testing and incident response. Co-founder and managing principal Paul Ihme describes the company's growth from there as organic, expanding into virtual CISO work, offensive security, managed detection and response, and Microsoft 365 security products.
Why LimaCharlie's AI Sessions works with any model

Co-founder and COO I have been using AI coding tools since the beginning. Back around 2022, I built a RAG system that would return links to relevant documentation when users made a search request. Initially, I wanted the AI to answer the user's question directly, but at the time it would hallucinate so much that I didn't trust the output enough to put it in front of users. Instead, I had the AI return static links to the relevant documentation.

Run LimaCharlie AI Sessions on the model you choose

Co-founder and COO AI Sessions in the LimaCharlie web application now run on OpenAI, Google Gemini, and OpenRouter models in addition to Claude. Connect your own credentials, pick a provider per session profile, and the session behaves the same way regardless of which model is doing the work. Sessions run on Claude by default. Beyond that, you can connect any of the following with your own credentials.

AI in the MSSP SOC: From Pilots to Production

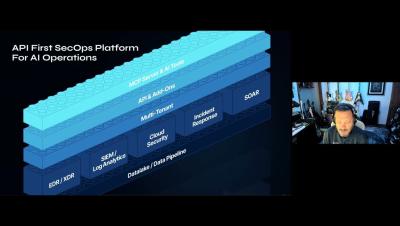
Every MSSP is under pressure to adopt AI, and most of the advice available is either vendor hype or generic guidance written for enterprise teams with one environment to manage. MSSPs face a harder problem: any AI they adopt has to work across dozens or hundreds of client stacks, respect tenant boundaries, and produce results an analyst can defend to a customer. In this session, Sr. Solutions Engineer Ken Westin lays out a practical roadmap for bringing AI into service provider security operations.

Intel Chat: Claude models reached real systems, an AI safety resignation & ShieldCrash [347]

Intel Chat with Matt Bromiley and Chris Luft. Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.

Intel Chat: OpenAI's Astra hits Critical, DEF CON phishing, Philippine nuclear breach [346]

Intel Chat with Matt Bromiley and Chris Luft. Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.

Intel Chat: OpenAI's Astra hits Critical, DEF CON phishing, Philippine nuclear breach [346]

Intel Chat with Matt Bromiley and Chris Luft. Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.

Threat Hunting to Detection Engineering, Part 2: Validating Rules Against Live Malware with Claude and LimaCharlie

Senior Solutions Engineer In Part 1, we looked at how to use Claude to analyze an unknown binary given a basic Linux system. Analysis is only half of the job, though, and while we can reasonably assume that our rules will work, especially for high-fidelity indicators such as hashes and IPs, rules looking for behaviors get more challenging to build and validate.

Ship a Working Detection Pipeline in One Workshop: Headless SOC with Grid by LimaCharlie

By the end of this hands-on workshop, you will have deployed a working detection pipeline, ingested a cloud log source, and shipped a bespoke dashboard app, all using Claude Code integrated with Grid by LimaCharlie. Along the way, you will see how Grid compresses the traditional SIEM/EDR/SOAR stack into a single automated workspace. We go well beyond standard EDR and SIEM use cases. What to expect.