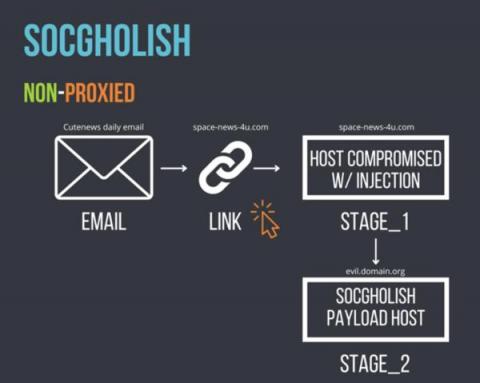
TA569 is a prolific threat actor primarily known for its deployment of website injections leading to a JavaScript payload known as SocGholish. In the past few months, Proofpoint researchers have observed changes in the tactics, techniques, and procedures (TTPs) employed by TA569. Changes include an increase in the number of injection varieties, as well as payloads deviating from the standard SocGholish “Fake Update” JavaScript packages.
You use your email address for a wide variety of things such as when you’re shopping or setting up an online account. Because your email is linked to so many different accounts, securing it is crucial to keeping your other accounts safe, since most password resets are sent to your email address. To make your email more secure you should create a strong password, enable MFA and always log out of your account.
Over the past few days, we have seen phishing attacks that use a combination of compromised Microsoft 365 accounts and.rpmsg encrypted emails to deliver the phishing message. At this stage, we are exploring and uncovering different aspects of this campaign and will share here some of our observations to date.