Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

SOCKS5 Proxy vs VPN What Each Actually Hides and When to Use Which

Online privacy tools often solve different problems despite similar marketing. A SOCKS5 proxy changes the route for selected traffic, and services such as nsocks.net can provide endpoints for applications that support this protocol. A VPN usually creates an encrypted tunnel that can cover most device traffic. Knowing the difference helps users choose without assuming either option makes activity invisible.
How Much Insurance Do You Actually Need? A Frugal Guide for Arizona Bar and Restaurant Owners

Frugal does not mean cheap for the sake of cheap. It means spending on the things that actually protect your money, and cutting the things that do not. Most of the advice in that category is about groceries, subscriptions, and whether you really need the name brand detergent. But there is a bigger, quieter category of "frugal" that a lot of small business owners skip right past: insurance coverage that matches the business you actually run, instead of the business you ran two years ago.

Which Cloud Misconfigurations Would an Attacker Actually Exploit First?

A cloud security dashboard can produce hundreds of configuration issues in a single afternoon. There are a few small housekeeping concerns. Some leave customer files or administrative tools open for strangers to access. Security teams need to know what findings need quick attention, yet they have limited time to examine.

Staying Private and Safe on Random Chat Sites

Talking to a stranger online has a pull that social media lost long ago. There is no feed and no follower count, just a new person and an empty chat box. That openness is also the risk. When you know nothing about the person on the other side, ideally they know nothing about you either, and keeping it that way is most of what staying safe comes down to.

Grandoreiro Malware: An Evolving Threat to Banking Customers

Grandoreiro is a malware family classified as a backdoor and spyware, first seen in April 2020, and is consistently described as a banking trojan focused on credential theft, remote fraud enablement, and control of compromised Windows systems. It has remained active through recurring campaigns, including a renewed wave in May and June 2026 that concentrated heavily on Latin America, especially Mexico, while also reaching parts of Europe and North America.

PHP2Shell and the end of the once-a-year pen test

On October 21, 2026, PHP shipped emergency fixes for two flaws that let anyone on the internet run code on a PHP web server, with no login. The weakness behind them had been flagged in 2024 and then sat, partly because nobody had proved it was exploitable. In 2026, researchers working with AI models proved it within days. Exploit attempts started before the fix shipped, and details leaked a day ahead of schedule. That sequence is the real story of PHP2Shell. The bug matters, but speed matters more.

Cybersecurity for Defence Networks: Protecting Critical Military Information and Systems

Digital technology plays an essential role in modern military operations. Defence organisations use interconnected systems to manage communications, exchange intelligence, coordinate personnel, and maintain operational readiness. However, increased connectivity also creates opportunities for cybercriminals and hostile actors to target sensitive information and critical infrastructure.

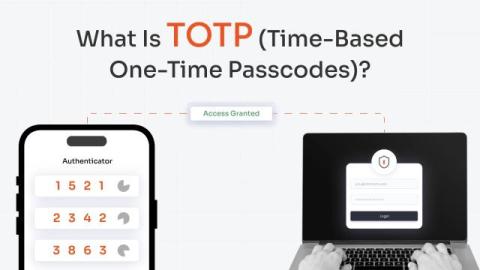
What Is TOTP? Security, Implementation, and Best Practices

TOTP (Time-Based One-Time Password) is an authentication algorithm that generates a unique, temporary numeric code using the current time as a moving factor. Typically, these codes are six digits long and automatically change every 30 seconds, providing a one-time verification code for authentication. TOTP uses a shared secret between the authentication service and the user's authenticator device, combining that secret with the current time to generate each code.

What is OAuth (Open Authorization)?

OAuth (Open Authorization) is an open-standard authorization framework that allows applications to access an end user's protected resources without requiring the user to share their password. Instead, users grant applications limited access to specific resources through authorization, while their credentials remain private. OAuth uses access tokens to control what an application can access on a user's behalf.