Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Destructive Malware: Threat Detection and Incident Response

Imagine that you have a snack you want to eat while watching a movie on a Friday night. You look in your kitchen, only to find the snack missing. Whether a roommate hid the snack or ate it, you no longer have access to it, disrupting your evening plans. This destructive behavior interrupts your weekend objectives, but it’s pretty low stakes overall.

ManageEngine recognized in 2024 Gartner Magic Quadrant for Security Information and Event Management for the seventh time!

We’re excited to announce that ManageEngine has once again been positioned in the Gartner Magic Quadrant for Security Information and Event Management (SIEM), marking the seventh consecutive recognition in 2024. ManageEngine Log360 is a comprehensive SIEM solution designed to help organizations effectively handle log data. It offers real-time threat detection, incident response, compliance management, and user activity monitoring.

Deciphering the SIEM Puzzle

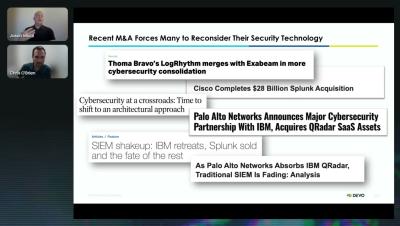
The 2024 Gartner Magic Quadrant for SIEM is here, jam-packed with 21 vendors. To add to the mix, recent mergers and acquisitions are stirring up the market. It’s no wonder security professionals are questioning their current SIEM’s future roadmap. But don’t worry—navigating this complex landscape doesn’t have to be overwhelming. We are here to help.

Never Miss a Critical Alert: Graylog 6.0 Elevates Security Alerting with Pushover Integration

Responding rapidly to cyber threats is a make-or-break capability in today’s high-stakes security environment. A missed alert can quickly escalate a minor incident into a major crisis, jeopardizing your organization’s critical assets and hard-earned reputation. A recent IBM study revealed that companies took an average of 237 days to identify a data breach in 2021 — an inexcusable delay that could invite catastrophic consequences. (Source: IBM Cost of a Data Breach Report 2022)

Credential Stuffing: How Cybercriminals Exploit Stolen Credentials

Credential stuffing is shaping up to be one of the most predominant hacking methods of 2024. In early June, Ticketmaster fell victim to a data breach via credential stuffing, exposing information from 560 million customers. Credential stuffing attacks involve using stolen usernames and passwords to access accounts. In these attacks, threat actors also often use automation to try different combinations of credentials until they find a successful match.

Meeting the Need for Speed in the SOC

Every day, in a high-stakes race against the clock, protectors must hunt down and stop threats before damage is done. As adversaries work faster and smarter, protectors must operate with greater agility. But legacy SIEMs are holding them back. Designed decades ago when log volumes and adversary speed were a fraction of what they are today, legacy SIEMs hinder investigations with agonizingly slow search speeds.

Considerations for Risk Rating Security Alerts

Security incidents and data breaches are the cybersecurity version of the definition of squares and rectangles in geometry. While all data breaches are security incidents, not all security incidents are data breaches. Before investigating an incident, many security teams know whether the alert will relate to a minor incident or a large-scale breach.

Introducing the SIEM of the Future: Splunk Enterprise Security 8.0

It’s been an exciting year for Splunk Enterprise Security! In May, we celebrated being recognized as a Leader ten times in a row in the 2024 Gartner Magic Quadrant for SIEM. We’re not stopping there. We’re excited to introduce the SIEM of the Future to keep the momentum going. Splunk Enterprise Security 8.0 is available now in a private preview.