Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Identifying Blind Spots Through External Attack Surface Management

Did you know that 69% of organizations have experienced some type of cyber attack in which the attack itself started through the exploit of an unknown, unmanaged, or poorly managed internet-facing asset? Understanding the scope of your organization’s external attack surface is essential. You need to continuously manage your digital footprint to know where risks exist and how to prioritize vulnerable areas. Gain visibility into what an attacker sees and take informed action to reduce exposure and empower your organization’s growth and success.

Optimizing Returns from Your Cyber Risk Program

In today’s economic environment, nearly every department in every organization across the globe is being challenged to do more with less. Meanwhile, digital footprints continue to grow and sprawl and cyber attackers look to take advantage of vulnerable infrastructure. Organizations need to assess how they can be more resourceful as they look to maintain a best-in-class cyber risk program and continue to meet business expectations.

CRQ Journey Part 3: Communicable, Calibrated, Granular Results

My journey to finding Kovrr had been packed with headaches and puzzles that many CISOs still face today. Within a few short years of being the CISO at Avid, a content-creation software provider, I managed to implement tighter security controls and develop a framework that enabled objective progress measurement. ‍ However, I constantly faced an impasse when attempting to communicate these achievements with the board.

Shadow IT: Managing Hidden Risk Across Your Expanding Attack Surface

One study found that 65% of SaaS applications in use are unsanctioned. And 59% of IT professionals find SaaS sprawl challenging to manage. In other words, shadow IT risks are growing—but that’s just the tip of the iceberg when it comes to hidden risks across today’s expanding attack surface. Missed software patches, outdated certificates, and stealth malware are some examples. Many security teams still struggle to keep their networks safe from ever-growing digital supply chains.

Understanding Data Lineage and Data Provenance

Data lineage and data provenance are related terms, but different. Lineage focuses on the origins and movements of data over time, while provenance focuses on the transformations and derivations of data from original sources. Provenance helps teams to follow the source of data and verify its authenticity, surfacing any potential risks or vulnerabilities. In other words, lineage is more about “where” data travels, and provenance is more about the “what” of data history.

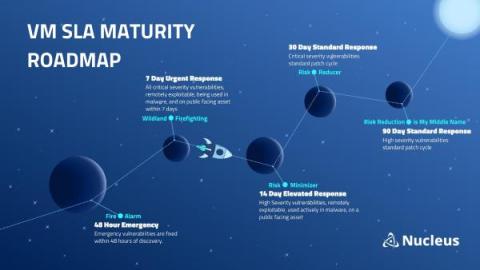
How to Adapt Vulnerability Management Service Level Agreements (SLAs) to Team Maturity

In working with customers across different enterprises and experiencing it myself, the challenges in managing vulnerabilities effectively are felt. Drawing from the insights of customers and my experiences, I’ve learned much about using Service Level Agreements (SLAs) in the vulnerability remediation process.

ShadowIT, Hidden Risk, and the insights that drive action to reduce exposure

The annual doctor wellness check always interests me. It’s generally the same routine every year: The doctor and I exchange pleasantries. She asks about any noticeable health changes while looking in my ears with that cool little penlight. If I’m lucky, she uses the mini-hammer to see how high my leg kicks after a gentle knee tap (I just love that for some reason). But it’s all a bit of a show, isn’t it?