Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Accelerating Threat Assessment and Risk Mitigation with Nucleus Vulnerability Intelligence Platform

In this webinar, discover how the Nucleus Vulnerability Intelligence Platform (VIP) is changing the way organizations handle vulnerabilities. Learn how VIP empowers security teams to assess, prioritize, and mitigate vulnerabilities in real time by leveraging automated workflows, comprehensive data aggregation, and custom risk ratings. Key topics covered: Chapters Don't forget to like, comment, and subscribe for more in-depth webinars and expert discussions on cybersecurity and vulnerability management!
Measuring Risk with One Yardstick: Lessons Learned on the Road to RBVM

How should we measure risk? Zebra Technologies has more than a dozen cybersecurity tools, thirty-five teams, and hundreds of people worldwide managing vulnerabilities. They wanted to measure with one yardstick; use a single, risk-based solution that could be customized to meet business criteria.

Predictive Vulnerability Management: Operationalizing EPSS with Business Context

Join us for an in-depth webinar on the Exploit Prediction Scoring System (EPSS), a powerful tool for predicting the exploitability of vulnerabilities. This discussion features experts Jay Jacobs from Cyentia and Stephen Schafferr from Peloton Interactive. They explore the intricacies of EPSS, its application, and the benefits of using EPSS over traditional methods like CVSS for better vulnerability management. Key topics include operationalizing EPSS, leveraging threat intelligence, and creating effective prioritization strategies. .

Triaging Non-CVE Vulnerabilities with Nucleus

Join Scott Kuffer, Co-Founder of Nucleus Security, in this webinar, focused on effective vulnerability management. Dive deep into the complexities of managing non-CVE based vulnerabilities. Learn about centralized vs. distributed remediation strategies and gain practical tips on triaging, prioritizing, and responding to vulnerabilities. This webinar emphasizes the importance of a unified approach to vulnerability management, leveraging threat modeling, and re-evaluating risk assessment methodologies to protect your business.

Building a Human-Centric Vulnerability Management Program

Steve Carter, CEO and co-founder of Nucleus Security, and Dr. Nikki Robinson, Security Architect at IBM, discuss the importance of the people side of vulnerability management. They explore challenges such as context switching, long mean time to remediation, and the impact of communication on vulnerability management programs. The conversation includes practical advice on incorporating human factors into cybersecurity practices, how to improve communication and collaboration among teams, and why understanding human factors is crucial for effective vulnerability management.

5 Things Holding Back Your Vulnerability Management Program and How to Overcome Them Step by Step

Welcome to our latest vulnerability management webinar, hosted by Scott Kuffer and Gene Bandy. In this session, Scott and Gene dive deep into the complexities and challenges faced by organizations in managing vulnerabilities and what you can do about it. Key Topics Covered: Why Watch This Webinar? Don't forget to like, comment, and subscribe for more in-depth webinars and expert discussions on cybersecurity and vulnerability management!
Vulnerability Management Benchmarking: Metrics and Practices of Highly Effective Organizations

This webinar dives deep into vulnerability management metrics, the challenges of maintaining cloud and ephemeral assets, and the discrepancies in vulnerability management across different organizations. Join us as we unravel the nuances of MTTR (Mean Time to Remediate), SLA (Service Level Agreements), and how high-performing organizations manage cybersecurity threats more efficiently. Don't miss this discussions on the role of data democratization in cybersecurity and how organizations can transition from reactive to proactive vulnerability management, no mature your VM maturity.

What Does a Solid VM Ticketing Workflow Actually Look Like?

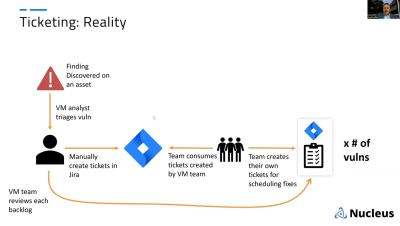
In this webinar, Scott Kuffer discusses the challenges and best practices of vulnerability management workflows and ticketing. He emphasizes the discrepancy between vulnerability management teams' priorities and the priorities of the business as a whole. Scott explores different ticketing workflows, starting with basic vulnerability-based tickets and progressing to more advanced options such as asset-based, team-based, and action-based tickets. He highlights the benefits of automating ticket creation and reporting, as well as the potential for redefining how vulnerability management is approached within organizations.

Visualizing Vulnerability Management: What Does a Single Pane of Glass Really Look Like?

Single Pane of Glass (SPOG) is a common buzzword that sends shivers down the spines of technical folks everywhere. Yet, executive teams ask for it, especially in vulnerability management. At the same time, the complex and fragmented nature of modern IT environments wreaks havoc on organizations aiming to understand their current location related to remediating and patching risks. So, what exactly is a single pane of glass, and what does it look like for enterprises today?

Applying Vulnerability Intelligence to CVSS and SSVC Frameworks

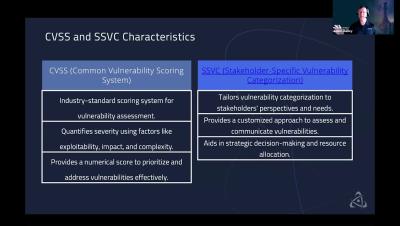
In this presentation, we explore the intersection of vulnerability intelligence and prioritization frameworks such as CVSS and SSVC as a means for strategically and rapidly prioritizing vulnerabilities to stay ahead of exploitation risks. We delve into the process of applying real-time threat intelligence tailored to the vulnerability landscape to enhance decision-making, optimize resource allocation, and ensure a precise and proactive defense against cyber threats.