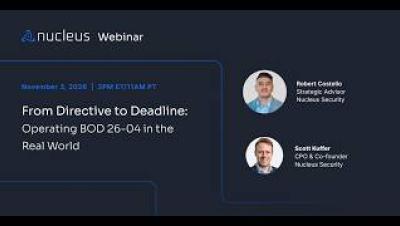
From Directive to Deadline: Operating BOD 26-04 in the Real World
BOD 26-04 changes how federal agencies and FedRAMP providers handle vulnerabilities. It moves away from severity-based, 30-day patching and toward risk-based prioritization. In this webinar, Bob Costello (former CIO of CISA, strategic advisor to Nucleus Security, and Chief Digital and Information Officer at The Merlin Group) and Scott Kuffer (Co-founder and CPO at Nucleus Security) explain what the directive requires, why CISA built it on the SSVC decision-tree framework, and how to put it into practice.