Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Future Is Cyber Risk Intelligence

Risk is expanding faster than most organizations can measure it, communicate it, and act on it. The convergence of AI, an ever-expanding attack surface, and deep, often hidden supply chain risks—extending into third-, fourth-, and fifth-party connections—all pose strategic and material risks to companies. Security leaders are ultimately looking for better ways to identify risk, prioritize action, and support stronger risk decisions across the entire business ecosystem.
Ransomware with a Twizt: Inside the Phorpiex Botnet

Phorpiex, also known as Trik, is a resilient and long-running botnet with a history dating back to 2011. While it has grabbed some headlines, its sustained presence and adaptability make it a subject of ongoing concern for the cybersecurity community. Phorpiex has consistently demonstrated its capability to evolve, shifting from a pure spam operation to a sophisticated platform.

AI Integration Security: Why the Biggest Risk Is Not the Model

When people talk about AI security risks, the conversation usually starts with the model. Can it be jailbroken? Can someone get around the guardrails? Can an attacker make it say or do something it should not? Those are fair questions, but they are not the most important ones. The bigger risk is not the model on its own: it’s everything the model is connected to.

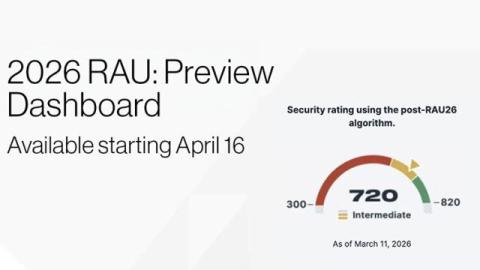
The 2026 Ratings Algorithm Update: Strengthening Accuracy and Stability

Each year, the threat environment changes, and the way we measure cyber risk has to keep up. Attackers adjust quickly. At the same time, organizations add cloud services, SaaS applications, and third parties to their environments. That makes it harder to maintain a stable, external measure of security performance. At Bitsight, the Ratings Algorithm Update (RAU) is one of the major initiatives that helps keep the Bitsight Security Rating a reliable indicator of security performance.

Major Security Event: Supply Chain Compromise in LiteLLM Versions 1.82.7 and 1.82.8

A supply chain compromise that impacted the Python package LiteLLM, with malicious versions 1.82.7 and 1.82.8 was published to PyPI on March 24, 2026. Bitsight Threat Intelligence, public reporting and vendor disclosures indicate the malicious releases included credential harvesting, Kubernetes-focused lateral movement, and persistence mechanisms, creating serious risk for cloud-native and AI-related environments that installed or ran the affected versions.

The Hidden Third-Party Risks Behind Domain Hijacking

Domains are foundational to digital trust. You visit your favorite online store or log in to your email without thinking twice about the web address in your browser. But what happens if that domain has been hijacked and you have just entered your personal information into an attacker’s trap?

From Risk to Resilience: A New Standard for Security Posture Management

For years, security leaders were asked a simple question: are we secure? Today, that question is harder to answer. Boards, regulators, insurers, and customers want proof of resilience: assurance that organizations understand their exposure, are prioritizing the right work, and are reducing risk over time.

Are AI Security Tools the New EDR? Attackers Are Treating Them That Way

AI security tools are no longer just defensive layers. They are high value targets being studied, fingerprinted, and bypassed much like traditional endpoint detection and response (EDR) platforms and antivirus solutions were in their early days. The speed and scale at which these tools are being deployed makes reactive defense increasingly unsustainable.

RondoDox Botnet: From Zero to 174 Exploited Vulnerabilities

According to a 2024 report from IoT Analytics, there were 16.6 billion Internet of Things (IoT) connected devices at the end of 2023, and that number is expected to grow to 41.1 billion by 2030. This means an increased attack surface for malicious actors to take advantage of, especially given that the security posture of the vendors that provide these devices varies greatly.

Connected Vehicles, Accelerating Risk: Inside the Cyber Threats Facing Automotive

The automotive industry is changing faster than ever, with smarter factories, connected vehicles, digital supply chains, and software-driven everything. But as the industry accelerates into this new era, something else is racing alongside it: cyber threats. Over the past year, Bitsight Threat Intelligence data has shown a sharp rise in ransomware activity targeting companies across the auto ecosystem. And what’s striking is how often the same names keep appearing.