Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Buying the Devices Is the Easy Part: The Complexity Behind Deploying Tech Across an Entire School District

Buying the tools is never the hard part. A district can approve a purchase order for interactive displays, robotics kits, or a cart of new devices in an afternoon. What's genuinely difficult, and what almost never gets talked about in the same conversation as the purchase, is everything that happens after the truck leaves: getting that equipment into forty classrooms, getting every teacher comfortable enough to actually use it, and making sure it's still being used well in April, not just during the excitement of week one.
Electronics Recycling Laws and Regulations: What Georgia Businesses Should Know

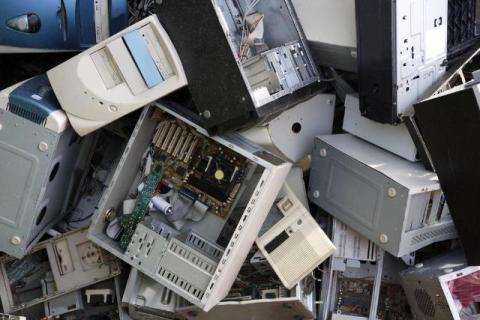
A lot of Georgia business owners hear "there's no state e-waste law" and quietly assume that means old computers and servers can go straight into a regular dumpster. That assumption is wrong, and it's an expensive one to get wrong, since the absence of a state law doesn't mean the absence of any law at all.

SCADA security: a practical guide for industrial environments

SCADA operations depend on recoverable servers and workstations as well as protected networks and controllers. A failed supervisory host can extend downtime even when field control remains intact. This guide maps the complete SCADA security stack and shows where PC-based backup and recovery fit without presenting Acronis as a SCADA network security platform. For broader OT and ICS foundations, see Acronis' OT and ICS cybersecurity guide.
Featured Post

Cyber Risk and Incident Response: A Growing Priority Across Industries

Cyber risk has become a dominant priority for organisations across nearly every sector. As the severity and velocity of the threat landscape and technological change continue to accelerate, organisations are under increasing pressure to ensure they can keep pace and recover quickly in the aftermath of a cyber event. A core focus for many organisations is strengthening their incident response capability: how effectively the business can react and recover when an attack occurs.

Dark Web Monitoring Vendors Compared

According to the 2026 Context Gap research, 79% of organizations first learn about active threats from outsiders rather than their own tooling. You've watched another headline roll past of a Fortune 500 company exposed on the dark web. Each story ends the same way: with a breach notification and inevitable board questions. You decide your company won't be the next case study. You need a tool that'll find your exposures before an attacker does.

Why do I need a cloud risk assessment?

Your business almost certainly runs on cloud services. From document storage, email and finance software to your customer data and internal systems, the chances are that most of what keeps your business operational lives, at least in part, in the cloud. And yet, for many businesses, the question of whether that cloud environment is secure rarely gets asked. It tends to be presumed. After all, you’ve got bigger things to worry about. You’re with a reputable provider.

When the fuzzers come knocking on port 389: Hunting injection canaries in LDAP

It's easy to think of core infrastructure protocols like LDAP, Kerberos, DNS, SMB, and NTP as furniture. They're so old, so ubiquitous, and normally so quietly reliable that we almost stop seeing them. However, history teaches us that Infrastructure protocols can and do have serious vulnerabilities. They say when you kick a rock over, dozens of bugs crawl out from under it. In this vein, this blog delves into how I went looking for one security issue and uncovered 6 other ones.

Why Buy a Mobile AppSec Platform Instead of Building With AI?

AI has lowered the cost of building mobile security tooling to near zero. However, it has not lowered the cost of operating it. Building a scanner is now a weekend project, while sustaining detection accuracy, threat research, real-device infrastructure, and developer trust across years remains a full organizational commitment. That distinction is the entire build-versus-buy question in 2026, and most evaluations get it wrong by measuring the wrong thing.

13 essential cybersecurity frameworks, standards, and regulations explained

Security teams rarely work from a single rulebook. They may use the NIST Cybersecurity Framework to organize the program, ISO/IEC 27001 to build a formal management system, SOC 2 reports to assess vendors, and laws such as HIPAA, GDPR, DORA, or NIS2 to meet legal obligations. Those names are often grouped together, even though they serve different purposes. Some provide guidance. Some can be certified or independently assessed. Others are contractual requirements, laws, or mandatory sector standards.