Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How SAML 2.0 Authentication Works?

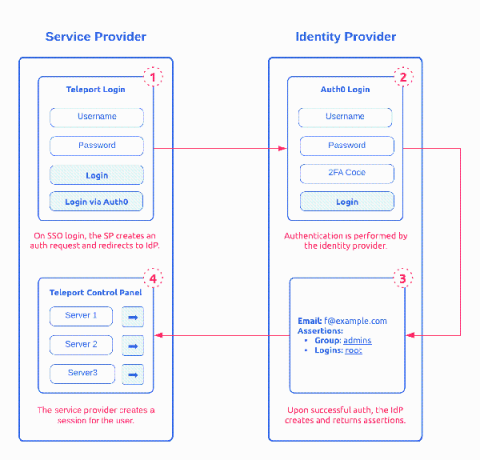
Security Assertion Markup Language (SAML) 2.0 is one of the most widely used open standard for authentication and authorizing between multiple parties. It’s one of the protocol that give users the single sign-on (SSO) experience for applications. The other adopted open standard is OAuth and OpenID. Of the two, SAML 2.0, released in 2005, remains the 800 pound gorilla in Enterprise SSO space. This post provides a detailed introduction on how SAML works.
Datadog acquires Sqreen to strengthen application security

We began our security journey last year with the release of Datadog Security Monitoring, which provides runtime security visibility and detection capabilities for your environment. Today, we are thrilled to announce that Sqreen, an application security platform, is joining the Datadog team. Together, these products further integrate the work of security, development, and ops teams—and provide a robust, full-stack security monitoring solution for the cloud age.

Python language support now beta in Snyk Code

Snyk Code now offers beta support for Python 2.x and 3.x projects. You do not have to install or update anything since we added the support to the backend engine and it is available instantly to be used. When a repository is scanned, you will see Python beta results showing up. If you cannot wait for a scheduled rescan, you can manually trigger a scan.

CloudCasa Now Supports Data Protection for Amazon RDS

The choice for persistent storage for your cloud native applications depends on many factors including how your cloud journey started and whether your applications were migrated or developed for the cloud. Also, depending on how early you started using containers and migrated to Kubernetes, your distribution or managed service may not have offered the persistent data services you needed.

Securing cloud native applications: ActiveCampaign's VP, Information Security provides perspective

Cloud native has been a growing trend as organizations shift away from on-premise infrastructure and longer software release cycles towards a more iterative development approach using cloud-based tooling and infrastructure. While cloud native applications enable rapid deployments and greater scalability, this emerging software approach also introduces security challenges.

Forrester's State Of Application Security Report, 2021: Key Takeaways

Forrester’s Annual State of Application Security Report has become a touchstone for organizations on their journey to achieve AppSec maturity. As the software development industry and threat landscape continue to evolve, Forrester’s State of Application Security Report for 2021’s main message is that while applications are still a major attack vector, analysts found signs of hope in their research.

How to fix Java security issues while coding in IntelliJ IDEA

Nowadays, developers are responsible for more than just creating the application. Besides working on features, developers have to focus on their applications’ maintainability, scalability, reliability, and security. Many developers are unsure of where to start with security. In addition, most companies still work with a dedicated security team instead of having security expertise inside the team. A lot of developers practically live in their integrated development environment (IDE).

Run confidently with secure DevOps

The rapid pace of digital transformation is accelerating the shift to cloud-native applications using containers and Kubernetes to speed the pace of delivery. But application delivery is one thing. Application uptime performance and protection are another. For cloud teams already running production one fact is clear, monitoring and troubleshooting are only the beginning. They also need to own security and compliance for their apps. In cloud-native DevOps is not enough. It's time for secure DevOps.