Security | Threat Detection | Cyberattacks | DevSecOps | Compliance


Introducing Teleport 10 Passwordless
https://goteleport.com/docs/access-controls/guides/passwordless/
0:00 Introduction to Passwordless
1:04 Passwordless in the Terminal
Teleport 10
0:00 Introduction
0:15 Passwordless Access
0:48 Access Requests
1:35 Snowflake Access
2:23 Teleport Server Access
3:15 Learn more
[Webinar] Detecting intrusion in DevOps environments with AWS canary tokens
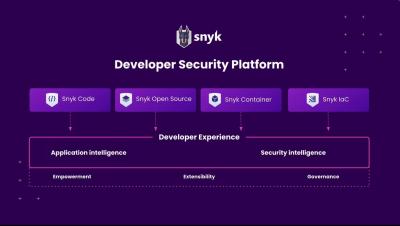
Snyk Demo in 20 Minutes | 2022
How attackers leverage example apps/reproduction scripts to attack OSS maintainers
A possible method of attacking your code base is a bit of social engineering that involves using open source to report potential bugs in software that provides reproduction applications. These applications can include malicious code that can compromise your software and applications. In the blog post, we’ll briefly look at why and how they operate, and how to mitigate this practice.
Production MySQL SSL with Teleport Machine ID
In the first part of this blog post, we setup SSL/TLS for a MySQL database, using the built in self-signed certificates. The main problem using out of the box self-signed certificates is that clients can't verify that they're talking to the right database host, and it's not possible to verify the certificate chain. In this post we'll cover upgrading the client connection to VERIFY_IDENTITY and how to use Machine ID to continuously renew certificates.