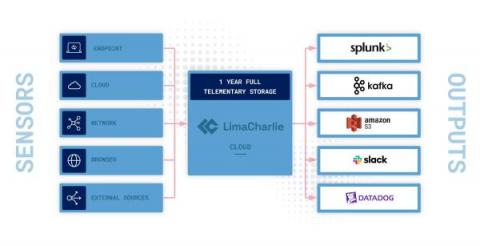
Security infrastructure as a service (SIaaS) is an engineering-centric, infrastructure-first approach to cybersecurity—and is at the heart of everything we do at LimaCharlie. In this post, we’ll explain more about what SIaaS is, why it’s important, and how it differs from legacy models of cybersecurity.
The White House and the Executive Office of the President have just issued a memorandum for the heads of U.S. government and federal executive departments and agencies for enhancing the security of the software supply chain through secure software development practices.
As cyberattacks become more sophisticated and frequent, developers and security teams often become overextended in their efforts to protect their software and applications. In an article for Security, Daniel Elkabes, Mend’s vulnerability research team leader, highlights what cybersecurity leaders should invest in now to help set up their teams for the future.
#policies
This video in the series describeshow the Mend Unified agent can be used to check and fail CI/CD pipelines when open source vulnerabilities and licensing risks are detected.
According to a recent Gartner study, the fast pace of change across technologies, organizational priorities, business opportunities and risks requires identity and access management architectures to be more flexible. As digital business relies on digital trust, security and identity are — more than ever — an essential foundation of an organization’s business ecosystem.