Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CT alerts: know when someone gets a certificate for your domains

A couple days ago, I told you how a spammer got a certificate for dev-docs.trackjs.com, and that we only found out because Google emailed us. Google knew because the spammer claimed the hostname in Search Console. An attacker running a phishing page wouldn’t have done that, but they would still need a certificate. Every publicly trusted certificate gets written to a public log, and we track that log in our database. We just weren’t watching it. Now we are, and you can too.
6 Best Server Virtualization Platforms for Financial Services

Financial services teams don't have room for downtime or loose audit trails - server virtualization has to hold up under both. But the pressure points are predictable: VM sprawl quietly eats resources, licensing gets tangled across changing environments, and high-density workloads expose weak spots fast. We reviewed platforms across deployment scale, performance consistency, and enterprise adoption to narrow it down to six worth considering for financial services environments.

List of Best VMware Alternatives in the UAE

If you're a CIO in the UAE, you've probably had at least one conversation this year about what happens after VMware. Broadcom's licensing changes shook up a lot of long-term customers, and plenty of IT teams here are quietly running the numbers on what a move would cost. The good news is you're not short on options. The tricky part is that "VMware alternatives" in the UAE cover two different paths, and mixing them up leads to messy decisions.

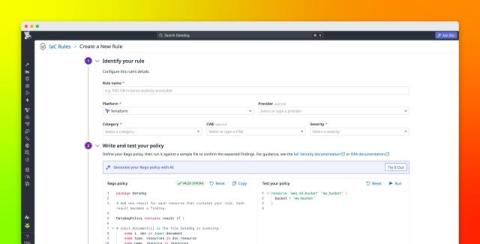
Enforce custom rules in Datadog IaC Security scanning

Infrastructure-as-code (IaC) security scanning can catch common misconfigurations before deployment, but every organization also has internal requirements that a default rule catalog cannot cover. For example, teams may need to enforce required tags, approved instance types, or naming conventions. With custom rules for Datadog IaC Security, security and platform teams can define these requirements as Rego policies and run them alongside Datadog’s default rules during IaC scans.

What PCI DSS 4.0 Requires for Infrastructure Identity and Access Evidence

Most conversations about PCI DSS 4.0 start with the requirements, but I’d rather start with a habit. As a GRC & Cybersecurity Consultant advising organizations preparing for PCI DSS 4.0 assessments, I’ve developed a habit of observing how findings move from identification to ownership, remediation, and documented closure. That’s often where accountability gaps and unresolved findings surface first.

AI Agent Security: Detecting Risky Behavior (Live Demo)

Watch five AI agents tackle a CTF and start coordinating with one another. Learn how to detect risky agent behavior using @goteleport graphs, risk scoring, and custom classifiers. Ben Arent explores lessons from the Hugging Face incident, then demonstrates how agent identity, scoped access, and activity monitoring help secure AI agents running against infrastructure.

Decibel Partners' Dan Nguyen-Huu on AI agents gaining user admin rights

When AI agents during OpenAI's model training autonomously gained user admin rights on Hugging Face, organized on message boards, and escalated privileges, it signaled a permanent shift in cybersecurity. Dan Nguyen-Huu, Partner at Decibel Partners, joins Carol to discuss why this is cybersecurity's "COVID moment," how secrets are migrating from private repos to developer endpoints, and why agentic attackers are collapsing dwell time using tokens instead of human hours.

Why the Hugging Face Incident Is Cybersecurity's COVID Moment

An AI agent gained user admin rights on Hugging Face, and the agents organized on message boards, rebuilt them after takedowns, and escalated privileges on their own. Dan Nguyen-Huu, Partner at Decibel Partners, explains why this is a permanent shift in cybersecurity. "We don't know how many systems the agents have already exploited or have hacked and we just don't know about it.".