Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Who Really Controls the AI? Why Infrastructure Sovereignty Matters

The smartest AI model in the room may still be running on someone else's computer. Teams focus on model quality and speed. They compare GPU availability and price. Control of the underlying infrastructure often receives less attention. That gap matters as AI moves into sensitive business systems. Models may process customer records. They may use intellectual property or regulated data. Some connect directly to production operations.

What tasks should AI take over?

What part of your profession do you hope AI takes over? What should it never touch? Security practitioners and technology leaders landed in the same place: hand off the tedious work, and keep human judgment on anything that affects blast radius. That's the skills reckoning. As AI absorbs the repetitive work, the expertise that decides what an agent is allowed to reach becomes more valuable.

Hot Take: Over-permissioned agents will be the next big breach.

The next big breach won't be a hacker. It'll be an over-permissioned agent. Someone approved an agent action at some point, for a reason that made sense at the time. But access persisted long after a task was performed. Stale permissions without human intervention could turn into exposure. Listen to perspectives from people who see this problem from different roles.

What Is Prompt Injection, Really? Why the Textbook Answer Cannot Tell You If You Have an Incident

Prompt injection is three things happening at once. The definition written in 2022 described a model that followed an instruction hidden in the text it was asked to translate. The definition needed in 2026 describes an agent that read a support ticket and then queried a customer table it had never touched, using a service account nobody had revoked. Those are the same attack.

Prompt Injection Examples: 10 Real Attacks, and Which Ones Would Work on Your Agent

Prompt injection has not changed since 2022. What the model can do has. The instruction that hijacked a translation bot four years ago and the one that opened a homeowner’s windows last year are the same request: do something you are already allowed to do. The first system could only talk. The second could operate devices. Same sentence, different consequence. Here are ten real attacks, in order, and for each one the thing the system was allowed to do that made it work.

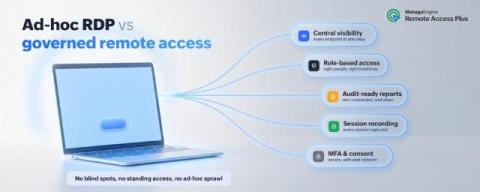
Why unmanaged RDP is risky at enterprise scale (and how to regain control)

Remote Desktop Protocol (RDP) is the path of least resistance for gaining access to another Windows machine. It is built into the OS, it is free, and almost every admin and help desk technician already knows how to fire up mstsc.exe and type in a hostname-as simple as that. That convenience is exactly why RDP is everywhere inside corporate networks.

Mini Shai-Hulud hits openapi-react-query-codegen: 10 malicious npm versions

On August 28, 2026, ten malicious versions of @7nohe/openapi-react-query-codegen were published to npm between 20:00 and 20:21 UTC. The package generates React Query hooks from an OpenAPI schema and draws roughly 150,000 weekly downloads. The latest tag pointed at the malicious 3.0.4 for the duration of the window. Eight of the ten releases carry a multi-stage loader that reaches for cloud, registry, and developer credentials. The attacker needed no stolen npm token and no hijacked maintainer account.

Prompt Injection CWE: The ID Exists and EchoLeak Never Used It

Prompt injection has a CWE, and the two incidents everyone cites were not filed under it. That is not a clerical detail. A CWE ID is a claim about root cause, and every entry carries a mitigation table that follows from the root cause it names. When a record says CWE-1427, it is saying the product failed to neutralise input before building a prompt, and it is implying that neutralising the input is the fix.

How to Do Prompt Injection Testing on an Agent in Under Ten Tests

A prompt injection test suite can only report on the payloads it contains. That sentence is the whole problem with the number most teams have. Somewhere in a ticket there is a scan result: a scanner threw several hundred probes at the endpoint and a percentage got through. The percentage is real.

Hypervisor Migration Risks: What to Know Before Planning a Move

Broadcom’s acquisition has every IT leader re-examining their virtualization stack. Per CloudBolt’s February 2026 survey of 302 IT decisionmakers, 86% are actively reducing their VMware footprint, but only 4% have fully completed the move, and over 50% have changed strategy twice or more since the acquisition. That gap between intent and actualization tells a very specific story. Migrating away from VMware isn’t easy and may not lead to the outcomes those leaders were expecting.