Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Adopting Zero Trust and SASE as Fed and SLED Agencies Go Remote-First

The global pandemic further accelerated a trend toward remote work that was already underway, even in federal, state, and local agencies that previously resisted it. But as agencies continue to offer telework options to employees, they must also rethink their security stack to better mitigate the cybersecurity risks that remote work catalyzes. Traditional, perimeter-based approaches to security will no longer work in a cloud-first environment where data can, and is, accessed from just about anywhere.
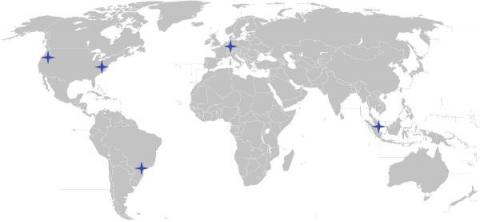
Low Latency Identity-aware Access Proxy in Multiple Regions

A multi-protocol access proxy is a powerful concept for securing access to infrastructure. But accessing numerous computing resources distributed across the globe via a single endpoint presents a latency challenge. Today we are announcing that the hosted edition of Teleport Access Plane is now available in 5 regions all over the world.

Netskope Private Access Demo - Browser Access (Clientless)

In this video, we will demonstrate the new client-less Browser Access capabilities in Netskope Private Access (NPA). We will walk you through the configurations and show you how to securely enable access to web applications for contractors, suppliers, and other 3rd party users as well as employee BYOD.

Netskope Selected to Participate in ATARC Zero Trust Lab

We are pleased to share that Netskope has been selected by the Advanced Technology Academic Research Center (ATARC) as one of 49 vendors to participate in its Zero Trust Lab. The Zero Trust Lab is a state-of-the-art physical and virtual test environment that will provide federal agencies with the opportunity to build, test, and evaluate new Zero Trust Architectures in a simulated environment.

Secure DevOps on Google Cloud: Reduce cloud and container risk

Google Cloud is helping businesses build and deploy apps faster than ever before, but at the same time, cloud teams must consider how to implement secure DevOps practices to avoid risk. We’re partnering with Google Cloud to provide security solutions to cloud teams to simplify safeguarding cloud and containers. Today, we announced our collaboration with Google Cloud.

How to meet 24 Google Cloud Platform (GCP) security best practices using open source Cloud Custodian and Falco

You’ve got a problem to solve and turned to Google Cloud Platform to build and host your solution. You create your account and are all set to brew some coffee and sit down at your workstation to architect, code, build, and deploy. Except… you aren’t. There are many knobs you must tweak and practices to put into action if you want your solution to be operative, secure, reliable, performant, and cost effective.

DLP Can Be So Much More Than Compliance

When you think about your DLP approach, what immediately comes to mind? Is it primarily centered around compliance? Is it simply using vendor-provided patterns of interest to satisfy an industry-specific framework like PCI, PII, or GDPR? Chances are, this probably describes at least some part of your DLP strategy because it is not difficult to set up and can satisfy a key business requirement of regulatory compliance reporting.