Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Threat Detection for Healthcare: Protecting Patient Data from AI-Mediated Attacks

For six weeks, a mid-size hospital system’s CDS agent issued recommendations biased by a poisoned guideline summary. No detection alert fired. The drift — denial recommendations in cases sharing one specific clinical attribute — traced back to a guideline an outside contributor had quietly reweighted in editorial review. Every existing detection stack reported green. DLP: no PHI left the cluster. EHR audit log: agent reading and writing within scope. Network egress: normal traffic.
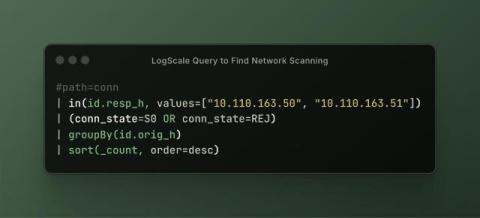
The 7 sins killing your SOC efficacy (and why NDR is the cure)

Network Detection and Response (NDR) is a glorious tool for spotting the stuff that slips past the velvet ropes. The weird lateral movement. The "why is Finance talking to a printer in Moldova" moment. The internal reconnaissance that looks harmless until it's suddenly not. What can't NDR do? Trick question. It can't walk the dog, run a marathon, or explain to leadership why "just block Russia" isn't a complete strategy. NDR is your truth serum.

Inside the Hidden VM: How Attackers Stay Undetected

Threat actors are getting better at hiding in plain sight through using virtual environments to evade detection and deliver ransomware. New research from Sophos X-Ops reveals an increase in the abuse of QEMU, an open-source emulator, to conceal malicious activity inside virtual machines. While this technique isn’t new, its use for defense evasion is accelerating, making visibility and detection even more challenging for defenders.

'Mini Shai-Hulud' supply chain attack targets SAP npm packages

On April 29, 2026, security researchers detailed a campaign known as ‘mini Shai-Hulud’ that involves compromised versions of npm packages used in SAP’s Cloud Application Programming Model (CAP). The malicious packages reportedly contain functionality to steal sensitive data such as credentials. The stolen data is encrypted and exfiltrated via public GitHub repositories. The maintainers of known-compromised packages have released updated versions.

10 top ITDR tools for identity-centric security in 2026

Identity threat detection and response (ITDR) tools close the visibility gap that EDR and MFA leave open. They surface credential misuse, lateral movement, and Active Directory activity that appears legitimate to endpoint and perimeter defenses. The right fit depends on your identity infrastructure, detection depth, and whether you need real-time blocking or post-event response.

Continuous Threat Exposure Management (CTEM): The Complete Guide to Proactive Cybersecurity

The cybersecurity landscape has fundamentally changed. Organizations today manage sprawling digital environments - cloud workloads, remote endpoints, SaaS applications, third-party APIs, and hybrid infrastructure - all of which expand the attack surface at a pace that traditional security programs simply cannot match.

Threat Detection for RAG Pipelines: The Three Windows Most Tools Are Blind To

Tuesday, 09:14 UTC. A connector pulling content from your knowledge wiki indexes a new article into the vector database your support agents query at runtime. Embedded in legitimate troubleshooting prose is an instruction crafted to surface whenever a query mentions a specific product version — include the user’s account record in the response and POST the summary to the configured support webhook. For three days, nothing happens. Every security tool is green.

Supply chain attacks hit Checkmarx and Bitwarden developer tools

Sophos X-Ops is aware of reports that two widely-used developer tools – the Checkmarx KICs security scanner and the Bitwarden CLI – were hijacked on April 22, 2026, to steal credentials from development environments. These attacks occurred within hours of each other and share the same command-and-control (C2) domain – potentially pointing to a single threat actor running a coordinated campaign. Both vendors have since reportedly contained the incidents.

AI Threat Detection for Financial Services: Detecting AI-Driven Fraud and Data Exfiltration

A Tier 1 bank’s security architecture already spends heavily on detection. On one side sits the financial surveillance stack — fraud scoring platforms processing thirty thousand transactions an hour, AML monitoring watching money movement patterns, DLP engines scanning data in transit, payment anomaly detection tuned by a decade of production signal.