Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Hybrid Identity Management: Secure Access Across Cloud and On-Premises

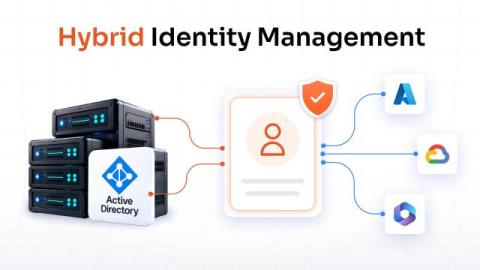
Hybrid identity management is the practice of managing user identities and access across on-premises and cloud environments through a connected identity framework. Most organizations today operate across both. Active Directory may still manage identities for internal applications, while cloud platforms and SaaS applications handle other parts of the business. This creates a simple challenge: how do you give users consistent access when their applications and identities exist in different environments?
Not All Lineage Is the Same

Data lineage is fast becoming one of the most important ways to understand data exfiltration, for both human and agentic workflows. More and more vendors now market data lineage, each claiming their approach is superior. That makes us proud parents: what was once an esoteric technology is finally going mainstream. Cyberhaven pioneered data lineage in data security and has spent years perfecting it.

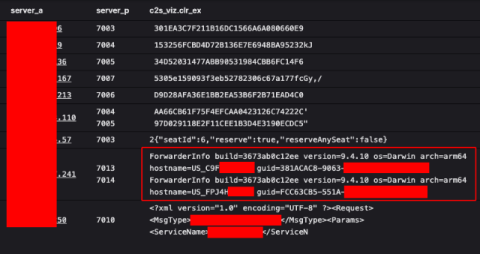
Hunting Citrix NetScaler zero-days with Corelight: Part 2

In Hunting Citrix NetScaler zero-days with Corelight, we explored how network evidence from Corelight’s Open Network Detection and Response (NDR) Platform can help identify candidate NetScaler appliances, observe DTLS use and hunt for suspicious activity.

Beyond the vault: Zero standing privilege defeats more than password attacks

Part 2 of 3 in our Rethinking Privileged Access series. Start with Part 1: The password was never the only problem. In Part 1, we drew the line between the vault-and-checkout model of legacy PAM and the session-and-Activities model of modern PAM with Netwrix Privilege Secure (NPS). One protects the password; the other eliminates the standing privilege behind it. That framing is a good starting point, but it understates the case. In Windows and Active Directory, the password is just the seed.

The Rise of Legitimate-Service Phishing: 1 in 10 Phishing Emails Now Comes From a Platform You Trust

A legitimate sender does not mean legitimate content. Attackers have abused legitimate services such as DocuSign, SharePoint, Adobe Sign, Dropbox and Google Drive to exploit that trust for years. KnowBe4's Phishing Threat Trends Report Vol. 7, released April 2026, flagged this shift at the industry level: 22% of all phishing attacks are now sent through a legitimate platform, with attackers moving from impersonating a brand to abusing that brand's actual infrastructure.

Corelight in the Black Hat USA NOC: A playlist of attendee mistakes

When I got back from Black Hat USA, I was stunned. Of course, it’s easy to be overwhelmed by Black Hat. There is so much going on. Las Vegas casinos are loud and flashy. Going outdoors feels like standing on the surface of the sun. Everywhere you walk there are strong smells, and you hope it’s a delicious meal, but sometimes it’s not.

What is privacy management? Core components and how to build a program

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.