Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Security Was Built for Humans. The Enterprise No Longer Runs on Humans Alone.

Cybersecurity has spent decades learning how to distinguish trusted users from attackers. The agentic enterprise complicates that model. An AI agent can be trusted, authenticated, authorized, and functioning as designed, yet still produce an unintended or risky outcome through a sequence of otherwise legitimate actions. That scenario does not require a malicious agent.

PII redaction vs. PII classification: why finding sensitive data is not enough

PII redaction and PII classification get used as if they were the same operation. They are not. PII redaction removes or replaces a value that a system has flagged as sensitive. Classification names what that value actually is, so a policy engine can select a rule for it. In an AI pipeline, the second step is the one that decides whether a policy can run at all. Short answer. PII redaction removes or masks a value a system has flagged as sensitive.

Rubrik MSP Unscripted - Episode 8, Part Two - Featuring Heejae Chae

In this episode of MSP Unscripted, we sit down with Heejae Chae from SysGroup to explore the evolving managed services landscape and what it takes for MSPs to stay competitive in a rapidly changing market. We discuss the growing importance of cyber resilience, the shift from traditional IT services toward outcome-driven managed offerings, and how MSPs can differentiate themselves by delivering meaningful business value to customers.

Rubrik MSP Unscripted - Episode 8, Part One - Featuring Heejae Chae

In this episode of MSP Unscripted, we sit down with Heejae Chae from SysGroup to explore the evolving managed services landscape and what it takes for MSPs to stay competitive in a rapidly changing market. We discuss the growing importance of cyber resilience, the shift from traditional IT services toward outcome-driven managed offerings, and how MSPs can differentiate themselves by delivering meaningful business value to customers.

CRA vs NIS2: Does Your Business Need to Comply With Both?

CRA vs NIS2: Which EU cybersecurity regulation applies to your business? Could your company face obligations under the Cyber Resilience Act, NIS2 Directive, or both? If your organisation develops software, manufactures connected products, or operates in a regulated European sector, understanding the difference between CRA and NIS2 is essential for identifying your cybersecurity compliance responsibilities.

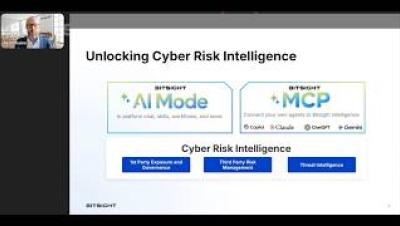
Bitsight MCP and Agentic AI Workflows: A Practical 90-Day Guide

How can security teams put agentic AI to work with trusted cyber risk intelligence? Discover how Bitsight MCP and Bitsight AI Mode help teams investigate cyber exposure, prioritize vulnerabilities, assess third-party risk, and automate security workflows. In this 45-minute webinar, Bitsight experts Christina Chehade and Tadd Hopkins demonstrate practical ways to bring AI into cybersecurity operations, from natural-language investigations to repeatable agentic workflows. You'll also get a 30/60/90-day roadmap for moving from initial exploration to scalable automation.

The Best AI Vendor Risk Management Tools in 2026

Conventional vendor risk tooling asks whether a supplier will suffer a breach. For an AI provider that question is necessary and incomplete, because the larger exposure is what the provider does with your material while operating exactly as intended. ‍ Retention periods, training use, inference location and the model serving an endpoint are data governance questions rather than security ones. Most platforms in this market have no field for them, which is the first thing to check. ‍

Cyber Risk Quantification Vendor Evaluation Checklist

Buying a cyber risk quantification platform means asking a vendor to defend numbers that will end up in front of a board, an auditor, or a regulator. Most evaluation calls never press that hard. The questions below are the ones that separate platforms from each other, and they are written so that any vendor can answer them, including vendors who would beat Kovrr on several of the answers.

Web App Owners - You're on Notice. Your Low-Hanging Fruit Just Got Lower

Recent incident response investigations reveal how AI-assisted attackers are chaining web application vulnerabilities, credential theft, privilege escalation, and lateral movement into autonomous intrusion workflows. This article is part of an ongoing series from Sophos frontline security operations specialists, sharing the expertise they use to strengthen our industry-leading Managed Detection and Response (MDR) service and defend customers against evolving AI-era threats.