Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Detecting silent sensors: Identifying EDR telemetry gaps with LimaCharlie

One of the most insidious security risks isn't a sophisticated attack, it's the endpoint that stops reporting. A sensor that appears enrolled but hasn't sent telemetry in hours or days represents a critical blind spot. Whether due to network issues, system shutdown, agent crash, or intentional tampering, these silent sensors deserve immediate attention.
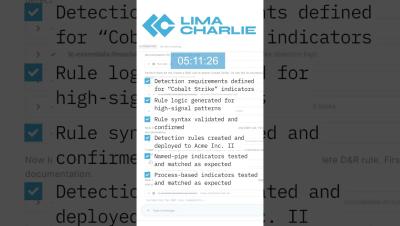
Claude Code writes and tests Cobalt Strike detection rules #cybersecurity #ai #securityoperations

Watch Claude Code generate production-ready Cobalt Strike detection rules in LimaCharlie. The agent defines detection requirements, creates rule logic for high-signal patterns, validates syntax, and deploys rules to the tenant. Named-pipe indicators and process-based signatures are tested against positive and negative controls to confirm accuracy. Security teams can operationalize threat-specific detections in minutes instead of hours.

Intel Chat: PeckBirdy, ShinyHunters, Moltbot impersonation & ELECTRUM [289]

In this episode of The Cybersecurity Defenders Podcast, we discuss some intel being shared in the LimaCharlie community. Support our show by sharing your favorite episodes with a friend, subscribe, give us a rating or leave a comment on your podcast platform. This podcast is brought to you by LimaCharlie, maker of the SecOps Cloud Platform, infrastructure for SecOps where everything is built API first. Scale with confidence as your business grows.

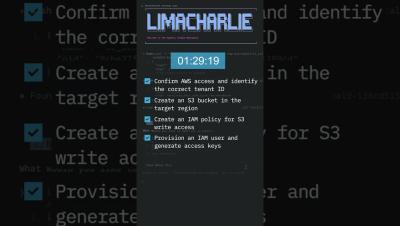
Claude Code configures AWS S3 export for security detections #cybersecurity #ai

Claude Code automates the entire detection export pipeline from LimaCharlie to AWS S3. The agent confirms AWS access, creates buckets with proper regional placement, provisions IAM policies with appropriate permissions, stores credentials securely, and enables continuous delivery. Security data flows from LimaCharlie to S3 for retention and analysis without manual AWS configuration.

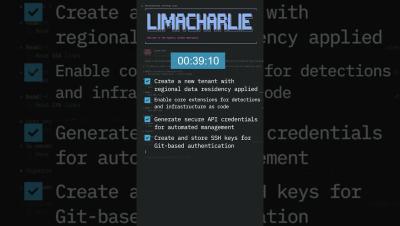
Claude Code builds security infrastructure with Git-based configs #cybersecurity #ai #secops

See Claude Code provision a new LimaCharlie security tenant with regional data residency, enable detection extensions, generate API credentials, create SSH keys, and establish Git as the single source of truth. Security teams can manage their entire LimaCharlie detection infrastructure through version-controlled code rather than point-and-click interfaces.

Threat hunting to detection engineering: Analyzing real malware with Claude Code, LimaCharlie, and Linux

Claude Code, originally just auto-complete on steroids for IDEs, shows a lot of promise for becoming a major tool in the DFIR/detection engineering/security analyst’s toolbox. Whether it’s Claude Code’s support of MCP, agent skills, or general ability to quickly figure out how to accomplish a given task, it is rapidly becoming more than a code generation tool. This is the first of a three-part series.

Agentic SecOps Workspace (ASW) office hours with LimaCharlie

Join us for a special Defender Fridays Office Hours session where the LimaCharlie team demonstrates the new Agentic SecOps Workspace (ASW) and explores what's possible when AI agents operate security infrastructure directly. At Defender Fridays, we delve into the dynamic world of information security, exploring its defensive side with seasoned professionals from across the industry. Our aim is simple yet ambitious: to foster a collaborative space where ideas flow freely, experiences are shared, and knowledge expands.

AI Action > AI Advice

Sr. Technical Content Strategist From Advisory AI to Operational AI in Security Operations The early wave of AI SOC platforms has delivered mixed results. While AI proved its usefulness as a triage assistant and next-step remediation advisor, these benefits came with significant drawbacks. Foremost, the cost of outsourcing an AI SOC is significant. Medium enterprises could expect to pay anywhere from $120,000 – $360,000 a year for the service.

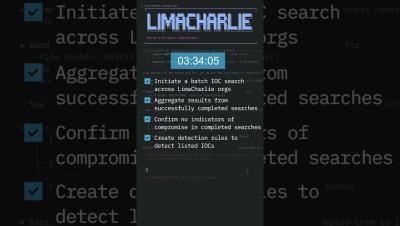
Claude Code reads a threat report, hunts for IOCs, and deploys detection rules #cybersecurity #ai

From threat intelligence article to deployed coverage. The AI agent extracts indicators, searches for compromise across tenants, confirms clean status, then creates and tests detection rules for ongoing protection within your LimaCharlie environment.