Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Continuous Compliance Monitoring: A Practical Guide

83% of organizations reported moderate or major delays from manual compliance work in 2026, while 53% said one full-time employee's worth of effort is spent on evidence collection, according to the 2026 State of Continuous Compliance Monitoring report. Those figures describe the operational problem more accurately than another promise of an audit-ready dashboard.

The Discrepancy Between the Results of Compliant Penetration Tests and What Really Defines an Organization's True Attack Surface

Organizations are investing large sums of money and resources in obtaining ISO 27001 certifications, SOC 2 attestations and performing yearly penetration tests, yet six months after the fact they hear about a breach involving one of their organizations in the media. This trend is so common, that many incident response professionals have used this as a recurring example when conducting post-breach analysis.
Featured Post

How Geopolitics is Driving Modern Cybercrime

Ransomware attacks no longer rely on traditional encryption methods. With today's advanced technology, threat actors are developing 'encryption-less extortion', focusing solely on data exfiltration and the threat of leaking or selling stolen sensitive information. Often used as part of double and even triple extortion strategies, ransomware has now evolved into a fragmented, competitive, and increasingly strategic threat landscape that employs divergent attack strategies, laser-focused on high-value targets.

Continuous risk monitoring in third-party risk management is non-negotiable: Here's why

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Legacy GRC can't keep up. Cyber risk assurance can.

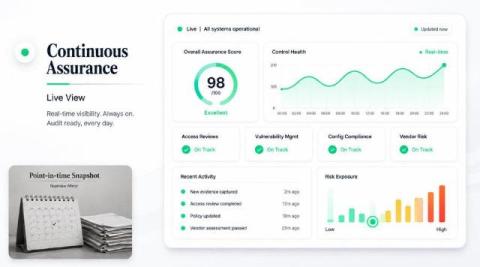
Enterprise security teams need to secure a risk surface that is constantly changing. However, the tools in their stack were built to check only a fraction of that risk. For confirmation, they rely on static snapshots and annual attestations. I now see this as the defining problem in GRC. When 451 Research (S&P Global) initiated coverage of TrustCloud in this space, they described a clear and growing divide.

What is RAR / FedRAMP Ready and is It Worth It?

FedRAMP has long been one of the more complex certifications you can achieve, but the rewards are well worth the effort. Validating your company's information security is a huge benefit, and on top of that, working with the government on sensitive contracts is a lucrative business venture. We do our best to explain various aspects of FedRAMP in plain English, to make it easier to figure out what your goals should be and where you should place your efforts.

Give your agents capabilities

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

The guide to HIPAA regulations and rules for healthcare companies and their vendors

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Run continuous compliance with Vanta

Plenty of tools can check a box at audit time. Vanta runs continuous compliance, so you're secure every day, not just the week before your audit. It runs on the Trust Graph, Vanta's data and intelligence layer that connects 400+ tools across your stack (cloud platforms, identity providers, task trackers, and more) and gives specialized agents the context to automate accurately. The difference isn't how many tools you connect. It's what happens after. In this video, you'll see Vanta in action.