Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

11 Questions You Should Ask About Your Cloud Security

The world is becoming more digital with each passing day. Many companies are trying to transition to an online or to a hybrid system, where they can offer flexibility and autonomy to employees and have a more efficient way of managing their day-to-day operations. The digital transformation to the online world requires businesses to invest in cloud computing and cloud security software.
Staying Connected with Cloud Exchange: Netskope Cloud Threat Exchange & Digital Shadows Plugin

Many technology professionals have experienced the sense of frustration that occurs when multiple tools in their environment do not play nicely with each other. When technology leaders are making decisions about bringing new tools into their environment, they should be thinking about more than whether the platform is just a shiny new object that adds a new capability to their team.

How To Identify and Stop a Phishing Attack

Phishing is a real problem. One that can wreak havoc on your digital and financial life. Here, we’ll look at different ways we can identify a phishing scam and stop it in its tracks. Phishing is the practice of sending emails (or other messages) with the intent to make the recipient believe it’s from a certain company or individual.

What Are Web Cookies? The Privacy and Security Risks of Internet Cookies

This article has nothing to do with chocolate chips or sprinkles. Sorry about that. Instead, we're talking about computer cookies and how too many web cookies can be bad for your online health. While cookies are enormously helpful and necessary for an easy-going web experience, they are not all good, and many pose some genuine privacy concerns. But what is a cookie, how does one work, and how do they (sometimes) infringe on your digital rights?

Securing SSH on EC2: What are the real threats?

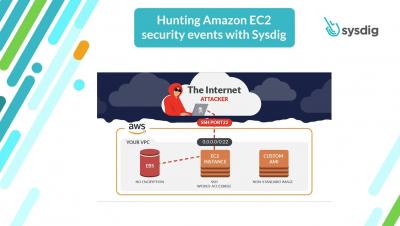
Every compliance audit will ask you to secure SSH, and every time a scanner checks the configuration or CSPM of your cloud account you’ll be warned for it. For example, if you don’t secure SSH on EC2, you’ll certainly get a critical alert stating that one of your Security Groups has its SSH port (22) open to the world. When this happens, you may think: Have I been pwned?

Securing cloud workloads in 5 easy steps

As organizations transition from monolithic services in traditional data centers to microservices architecture in a public cloud, security becomes a bottleneck and causes delays in achieving business goals. Traditional security paradigms based on perimeter-driven firewalls do not scale for communication between workloads within the cluster and 3rd-party APIs outside the cluster.