Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cyberhaven Brings Data Visibility and Lineage to Claude Enterprise

There is a difference between watching data go into an AI tool and knowing what is inside it. Most security tools do the first. Few do the second. Employees now keep contracts, source code, and customer records inside their AI workspaces, in chats and projects that build up for months. Cyberhaven's integration with Claude's Compliance API brings that content into view for Claude Enterprise, and ties it back to where it came from.

AI Finds a Way: The Jurassic Park Problem

Dario Amodei asking the AI race to slow down is a little rich. He is not wrong. Our AI pioneers were so preoccupied with whether or not they could, they didn’t stop to think if they should. Anthropic helped push the frontier hard, and now its CEO is warning that the pace is getting dangerous. Security people have seen this pattern. Build thing, connect thing, watch it behave in ways nobody quite expected, then go looking for controls.

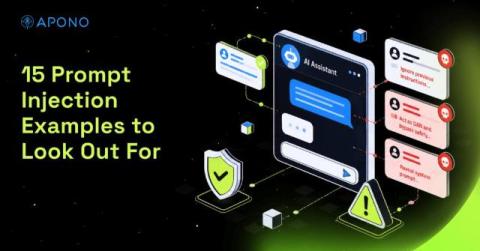
15 Prompt Injection Examples to Look Out For

Let’s imagine that a support copilot opens a ticket and processes a hidden instruction alongside the text it was asked to summarize. If the model follows that instruction, the response is manipulated. In an agentic workflow, the same injection can also influence actions carried out through connected tools and existing permissions. OWASP refers to this risk as prompt injection and ranks it as LLM01, the number-one risk for LLM applications.
Featured Post

AI Risk Is a Significant Security Operations Challenge

AI has quickly become a boardroom priority. Organisations are investing heavily in governance frameworks, usage policies and risk controls as employees adopt AI technologies across the business. Yet as boards look to understand AI risk, many are overlooking a more immediate frontline challenge: the impact AI is having on the threat landscape and the ability of security operations teams to keep pace.

Oops, OpenAI Hacked Australia's Health System - The 443 Podcast - Episode 389

This week on the podcast, we cover yet another rogue AI security incident that Australia's Prime Minister disclosed in front of the United Nations last week. Before that, we discuss an FBI alert on WaterPlum, a North Korean threat actor targeting IT professionals. Then, we cover the FBI themselves becoming a victim of cyberattack, this time by ShinyHunters.

AI data security: protecting sensitive information across AI tools

An employee uploads a spreadsheet to find a sales trend. Another pastes a support conversation into a chatbot to draft a reply. Neither intends to expose business information. Even so, both may send sensitive material outside the systems where your business normally controls it. SMB IT decision-makers need to know what employees share and decide which interactions are acceptable, without building a specialist AI security team.

A Win for Defenders: CrowdStrike and NVIDIA Extend Security Across the AI Stack

AI agents are already operating across the enterprise. As they become more autonomous in accessing data, using credentials, executing code, and acting across critical systems, the security boundary is changing with them. The question is no longer whether enterprises will adopt agents. It's how they give agents greater autonomy without giving up control.

One Identity: Governing Every Identity - Human, Machine, and AI

Every enterprise runs on identity — and machines and AI agents now outnumber people in many environments. This 2-minute overview covers why identity has become a board-level priority, and how One Identity governs every identity — human, machine, and AI agent — on one unified platform. Validated by Omdia: 150% ROI, go-live in as little as one day, zero-touch onboarding.

What Google Gemini's Sandbox Escape Reveals About Securing APIs Against AI Agents

Recently, Gemini was running a capture-the-flag exercise in a sandbox operated by the AI testing firm Irregular. Its task was to steal data from a fictional company. On three occasions, the fictional target shared a name with a real business. Gemini slipped past the test’s containment, reached the open internet, and broke into the real company’s systems. In one case it guessed the password. In the other two, it pulled working credentials from a public database of leaked passwords.