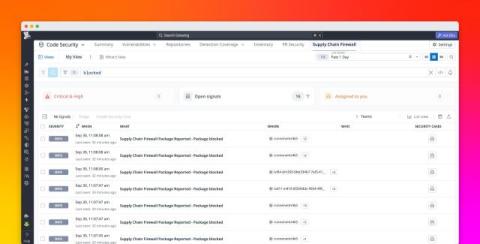
Block malicious packages across your organization with Supply Chain Firewall and Datadog Code Security
Campaigns such as Shai-Hulud 2.0 have demonstrated how quickly package malware can propagate through npm and then harvest credentials. Traditional dependency scanning can identify known risks in code once a package is added to the code, but security teams also need a check before installation.