Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Does NIS2 Apply to Your Organization Ask These 5 Questions

Many organizations assume the NIS2 Directive only applies to large enterprises based in Europe. In reality, organizations with operations, customers, suppliers, or digital services connected to the EU may also have cybersecurity compliance obligations. In this short video, we cover five practical questions that can help determine whether your organization may fall within the scope of NIS2. You'll learn.
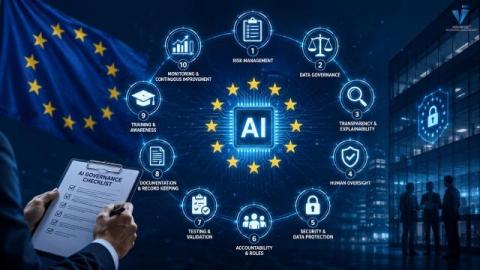
EU AI Act Readiness: 10 Controls Every Organization Should Implement in 2026

This is for compliance and security leaders who already know the EU AI Act applies to them and need a concrete control set for where the law actually stands today — not a summary written before the rules changed. Awareness is done; 2026 is the year of implementation, and the rules just moved. On 29 June 2026 the Council of the EU gave its final green light to the Digital Omnibus on AI — the package that resets several of the dates compliance teams have been building toward.

ISO 27001 vs ISO 42001 Do You Need Both

Already certified to ISO 27001 but wondering if your organization also needs ISO 42001? In this video, we explain the difference between ISO 27001 (Information Security Management) and ISO 42001 (AI Management Systems). If your organization uses AI tools like ChatGPT, Microsoft Copilot, Gemini, or develops AI-powered products, understanding AI governance is becoming increasingly important. Learn when ISO 42001 complements ISO 27001 and how both standards help organizations strengthen security, governance, and compliance.

How Long Does ISO 42001 Certification Actually Take? A Realistic Timeline

ISO 42001 certification usually takes four to twelve months. This runs from the gap assessment to the certificate. For a 50 to 200-person organization, first-year costs are about $85,000 to $150,000. Businesses with an existing ISO 27001 system can often certify in three to four months. This guide is for compliance and AI leaders planning an ISO 42001 project. It gives a realistic timeline and budget, not a vendor’s best-case pitch.

EU AI Act vs ISO 42001: What's the Difference - and Do You Need Both?

If your business builds or uses artificial intelligence, two names often come up. They are the EU AI Act and ISO/IEC 42001. They are easy to confuse, and getting the relationship wrong either wastes budget or leaves you exposed. This guide explains what each one requires, where they overlap, and how they work together.It shows how compliance leaders, CISOs, and AI product owners can use them without repeating work.It also helps you avoid gaps that could lead to an audit failure. Contents.

GDPR Compliance for Small Businesses: The Complete Guide

GDPR compliance for small businesses means having a documented, evidence-based process for how you collect, use, store, and delete the personal data of EU residents — regardless of your company’s size, revenue, or location. This guide walks through all ten compliance domains regulators expect you to have covered: data mapping, lawful basis, privacy notices, data subject rights, privacy by design, retention, vendors, transfers, breach response, and governance.

DPO as a Service UK: Enhance Data Protection & Compliance

UK organisations need continuous UK GDPR and EU AI Act compliance, and most cannot justify the cost of a full-time hire to deliver it. Here is how DPO as a Service closes that gap — and what to look for in a provider. Contents hide What Is DPO as a Service? Why UK Organisations Need a Data Protection Officer The Cost of Getting This Wrong: Two 2025 Enforcement Cases Key Benefits of Outsourcing Your Data Protection Officer How DPO as a Service Ensures Ongoing Compliance.

Best Practices for Secure Credit Card Storage

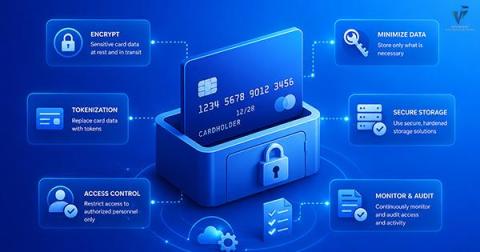
Businesses must never store CVV/CVC codes, full magnetic stripe data, or PINs under any circumstances. For PANs that must be retained, use AES-256 encryption with hardware security modules (HSMs) or, better yet, replace card data entirely with tokens via a PCI-DSS-compliant third-party vault. This removes raw card data from your environment and reduces your compliance scope from SAQ D (hundreds of controls) to SAQ A (as few as 22 controls).