Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What Is the Role of Privileged Access Management in Protecting Sensitive Data?

Privileged Access Management (PAM) plays a crucial role in protecting sensitive data by controlling, monitoring and limiting access to systems and accounts. PAM focuses specifically on managing accounts with elevated permissions, such as administrator or root accounts. These accounts, if compromised or misused, can pose significant security risks and potentially lead to severe data breaches.

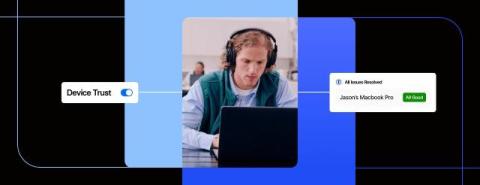
Enforce device posture beyond SSO with Extended Device Compliance

At RSAC 2025, we announced Extended Device Compliance, a new capability within 1Password Device Trust that enforces device posture Checks before allowing access to web applications, including those not protected by single sign-on (SSO). Extended Device Compliance redefines industry expectations for device trust solutions, ensuring devices are secure and compliant even when users access apps outside traditional admin control.

Device security beyond MDM: Why Omdia recommends Extended Access Management

Omdia, a global analyst and advisory leader, recently released a report called “How Extended Access Management (XAM) closes the gaps in security.” The report defines the challenges of modern access management as: These unmanaged forms of access create an Access-Trust Gap: The security risks posed by unfederated identities, unmanaged devices, applications, and AI-powered tools accessing company data without proper governance controls.