Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to prevent ransomware damage: a 12-step checklist for IT teams and MSPs

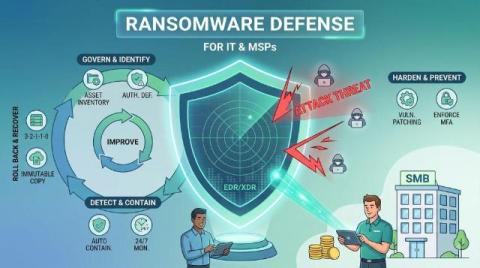
No combination of controls guarantees that ransomware actors will never gain access or cause any impact. What the 12 controls below do is reduce the attacker's opportunities, accelerate containment and preserve the ability to restore operations without relying on ransom payment. Think of ransomware resilience as a continuous lifecycle rather than a fixed sequence: govern and identify, harden and prevent, detect and contain, roll back and recover, and improve and patch.

AI Governance Tools and the Audit Trail Problem

An AI governance platform demo shows you the present. Compliance posture at seventy-nine percent, four controls needing attention, a register of systems with owners attached. Every figure describes today, and the demo is persuasive precisely because today is legible. ‍ An audit asks a different question.

7 Things People Get Wrong About Quantifying Cyber Risk

Most explanations of financial cyber risk modeling cover what it is. The more useful material is what surprises people once they have a model in front of them, because several of the outputs run against intuition and get misread in predictable ways. ‍ Seven of those are worth knowing before the first results arrive. None requires a statistics background, and each one changes how a number should be read or reported. ‍

Tactics Techniques and Procedures TTP: A 2026 Guide

Tactics, techniques, and procedures are the behavioral language of an adversary: tactics explain why, techniques explain how, and procedures describe the specific implementation. MITRE created the first ATT&CK model in September 2013 and publicly released it in May 2015 with 96 techniques organized across 9 tactics. That origin matters because TTPs turn scattered security events into an operational model.

Ransomware protection for businesses and MSPs: the complete guide

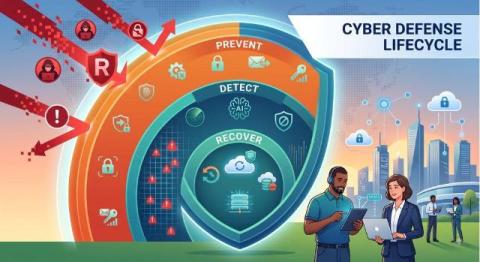
Ransomware protection is a coordinated set of controls that reduces the likelihood of compromise, detects and contains malicious activity, protects recovery infrastructure and restores operations when an attack succeeds. It spans identity security, vulnerability and patch management, endpoint protection, EDR or XDR, incident response, targeted rollback, immutable backup and disaster recovery. No single control covers the complete ransomware lifecycle.

OpenTelemetry and AI Governance: Where the Standard Stops

OpenTelemetry graduated from the Cloud Native Computing Foundation in May 2026, which formally settled a question the industry had answered informally years earlier. It is the standard way applications emit telemetry, second only to Kubernetes in contributor volume, and native across every major observability backend. ‍ A security and governance company has a specific reason to care.