Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Securing the Agentic Enterprise with Behavioral Analytics and AI Visibility

By mid-2026, the question is no longer whether AI belongs in the enterprise. It’s already embedded in daily work, supporting research, development, customer engagement, and operations. AI agents now act on behalf of employees, automate decisions, and interact directly with enterprise data and systems. This shift creates a new security challenge.
Unlock Compliance Management Solutions for 2026

You can usually tell when a compliance program is still running on audit season logic. Three weeks before an assessment, Slack fills with evidence requests. Security exports screenshots from cloud consoles. IT pulls user lists from IAM. HR scrambles to prove termination workflows. Someone opens the spreadsheet nobody has touched since the last audit and starts guessing which controls still map to which systems.

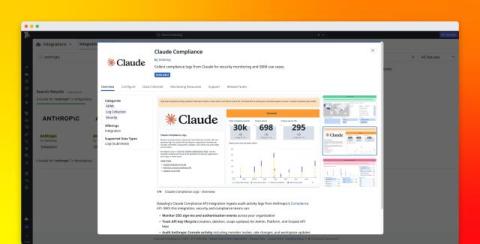
Monitor Claude Enterprise activity with Datadog Cloud SIEM

As Claude adoption expands across enterprises and workflows, security and compliance teams need to understand who is using Claude Enterprise, how it is accessed, and how it is administered and configured across the organization. The Claude Compliance API gives organizations access to valuable activity data that supports security monitoring, investigations, and governance initiatives.

AI Quality EXPLODES Unlock Productivity SECURELY & FAST! #podcast #cybersecurity

On this episode of Masters of Data, Adam White and David Girvin dig into Sumo Logic's freshly launched compliance apps for Claude, ChatGPT, and LiteLLM, and why your IT team will want to pay attention before the token bill arrives. We unpack how enterprises can move beyond the "AI black hole" era of shadow IT and actually get eyes on who is using what, how much it is costing, and whether any of it is moving the needle.

AI is a NEW Gold Rush But Token Burn is STUPID! #podcast #cybersecurity

On this episode of Masters of Data, Adam White and David Girvin dig into Sumo Logic's freshly launched compliance apps for Claude, ChatGPT, and LiteLLM, and why your IT team will want to pay attention before the token bill arrives. We unpack how enterprises can move beyond the "AI black hole" era of shadow IT and actually get eyes on who is using what, how much it is costing, and whether any of it is moving the needle.

LLMs Data Spies or Security Nightmares #podcast #cybersecurity

On this episode of Masters of Data, Adam White and David Girvin dig into Sumo Logic's freshly launched compliance apps for Claude, ChatGPT, and LiteLLM, and why your IT team will want to pay attention before the token bill arrives. We unpack how enterprises can move beyond the "AI black hole" era of shadow IT and actually get eyes on who is using what, how much it is costing, and whether any of it is moving the needle.

The Four Environments Where SaaS-Only SIEM Fails

Picture a cybersecurity team responsible for protecting a classified military installation in a remote operational theater. No internet connection. No cloud services. Classified and unclassified networks running on physically separate infrastructure. Their security information and event management system has to detect threats, correlate events, and generate alerts with zero external connectivity, for the entire deployment. That is not a compliance checkbox. It is a physics problem.

Centralized Log Management: Guide, Compliance & Blueprint

A security alert rarely fails because the team lacks data. It fails because the data is scattered. At 2 a.m., that usually looks familiar. The firewall has one timestamp format. The domain controller has another. The cloud console keeps the event you need behind three menus. The application server writes plain text that only one engineer knows how to read.

HIPAA Compliance Automation: Roadmap for CISOs 2026

Most healthcare security teams don't start thinking about HIPAA automation because they love compliance tooling. They start when another audit request lands, someone asks for six months of access reviews, policy attestations are out of date in three different folders, and the security team spends a week reconstructing evidence that should already exist. The problem isn't that teams don't understand HIPAA.

Agentic SOCs: The public sector's new AI cybersecurity defense

Adversaries are using AI to launch cyber attacks in record time, forcing security teams to measure responses in seconds instead of hours or days. Detecting these attacks is increasingly difficult. Phishing campaigns built by large language models (LLMs) achieve click-through rates 4.5x higher than traditional methods.1 Public sector organizations are at an inflection point with cybersecurity. Most security stacks in place today weren’t built for this level of speed.