Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Autonomous Pentesting: AI Agents That Test Your App 24/7

Most companies pentest their app once a year. Hackers look for new backdoors every single day. Astra Autonomous Pentesting closes that gap with AI security agents that test your web app continuously, 24/7. Traditional penetration testing gives you a giant report full of jargon that sits on a shelf. Astra works like a friendly hacker that never sleeps. When it finds a security weakness, it doesn't just send a scary alert. It explains the exact problem, with the attack story and proof, so clearly that AI coding tools can fix, test and repair the vulnerability the same day.
Continuous Attacker Emulation: Testing Controls Between Annual Assessments

Security controls are built to stop attackers, but most organizations only find out whether those controls actually work once a year, during a scheduled assessment. In the months between those engagements, configurations change, new tools get deployed, and remediation work from the last test either holds up or quietly fails without anyone noticing. Continuous attacker emulation exists to close that gap, giving security teams an ongoing read on their actual exposure rather than a single snapshot frozen in time.

Penetration Testing vs Red Teaming: Choosing the Right Approach

When you're assessing a building's level of security, you're not just looking at one thing. It's great knowing that the front door has a series of unpickable locks bolted onto it, all of which have only one key in existence, but it's not really going to do anything if you're missing an entire external wall, essentially turning your living room into an open deck.

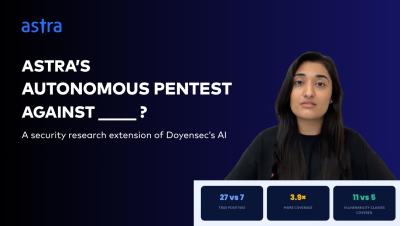
Astra's Autonomous Pentest Against Other Tool

Astra vs. Other Tool: Who Finds More Real Vulnerabilities? How does Astra Autonomous Pentesting compare with the other tool when it comes to finding real-world vulnerabilities? In this independent benchmark, Astra was tested against the other tool to evaluate vulnerability coverage, depth, and true-positive findings. The results: 27 true-positive vulnerabilities identified 3.9× more vulnerability coverage 11 distinct vulnerability classes discovered Deep testing across business logic and application behaviour.

Agentic AI-Assisted Penetration Testing: AI Scale. Human Precision

When Mythos launched, headlines warning of its potential dangers were prolific. For security risk leaders, it felt like a watershed moment, one that signaled that AI had arrived, but simultaneously raised widespread concern about risk. Many wanted to understand how real the risk was for their organization and what should be done about it.

Can Autonomous Pentesting Rescue CVE Coverage From Vanity Metric Hell?

The security industry killed CVE coverage as a credible metric, and it deserved to die. Vendors inflated the numbers for years in the name of depth, and nobody in the room had an incentive to ask whether they reflected real validated risk or just a longer signature list. So “CVE coverage is a vanity metric” became earned consensus. The question I keep coming back to is whether the autonomous pentesting era makes that consensus outdated.

Autonomous Pentesting Is About To Kill Security Abbreviations

I have watched the security industry run a very profitable game with abbreviations for the last decade. The simple way to do it is to invent a category, give it a cool catchy abbreviation, market it as the missing piece of the stack, and repeat. The greatest examples are CTEM, BAS, ASM, and EASM. Every one of them arrived promising to close the gap the last one left open, and every one of them ended up as a line item on a renewal spreadsheet that nobody at the buyer‘s side could confidently defend.

Chaining Vulnerabilities into Attack Vectors with Autonomous Pentesting

Your vulnerability report is sorted by severity. The adversary looking at the same environment is sorted by path. That mismatch is the whole problem. Open any scanner output, and you get a tidy hierarchy: criticals at the top, then highs, then a long tail of mediums and lows that most teams will never touch. To the person who wrote the ticket, that tail is noise. To someone who thinks in chains, it’s a roadmap. A page of “lows” is not a page of things you can ignore.

Autonomous Pentesting to Vet Vendors at Scale in 2026

Somewhere in your vendor list, right now, there is a door you have never checked. You didn’t build it, you don’t hold the key, and yet if someone walks through it, the breach notification goes out on your letterhead. The numbers too aren’t subtle. Verizon’s 2026 Data Breach Investigations Report found that 48% of breaches now involve a third party, up from 30% just a year earlier, the sharpest rise the report has ever recorded. Your vendors are your attack surface now.