Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

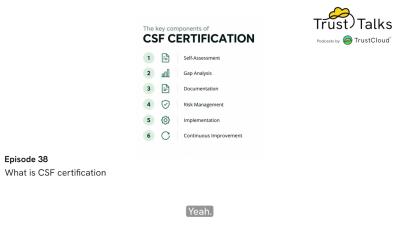
What is CSF certification | TrustTalks - Ep 38

Organizations across industries are constantly challenged to protect their sensitive information and manage potential risks effectively. CSF certification, short for Cybersecurity Framework certification, has emerged as a significant marker of an organization’s readiness to face cybersecurity challenges while ensuring compliance with industry standards. In this podcast, we explain what CSF certification is, examine its origins and benefits, and offer insights into how organizations can achieve and maintain this critical certification.
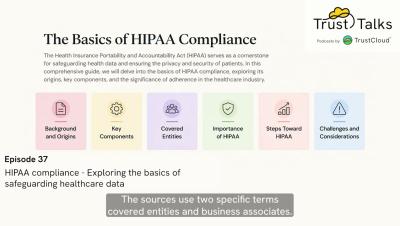
HIPAA compliance Exploring the basics of safeguarding healthcare data | TrustTalks - Ep 37

With digital health records and telemedicine becoming the norm, safeguarding patient information is more critical than ever. The Health Insurance Portability and Accountability Act (HIPAA), enacted in 1996, serves as the cornerstone of healthcare data protection in the United States. Designed to ensure the confidentiality, integrity, and availability of Protected Health Information (PHI), HIPAA sets national standards for healthcare providers, insurers, and their partners. Compliance with HIPAA not only mitigates legal and financial risks but also fosters trust between healthcare organizations and patients.

Becoming the board-ready CISO: First steps for effective conversations (Alyssa Miller)

Becoming the board-ready CISO: Alyssa Miller on what boards actually want from security, and a three-part framework any CISO can use to align security with business objectives. CISO and Board Advisor Alyssa Miller joins TrustCloud CEO Sravish Sridhar to challenge the idea that “security first” is the right frame, and to lay out how strategic CISOs report to the board: mapping security to business objectives and KPIs, focusing on the few resilience goals that matter, and making the case for new investments like AI as business value, not just risk.

CISOs - Transforming third-party risk assessments

CISOs struggle with third-party risk assessments. Automate third-party assessments and eliminate mundane tasks. Use AI and API driven automation to accelerate and simplify first-party, third-party, and nth-party risk assessments. Automate document analysis and receive contextual, reliable information. Run frequent, programmatic risk assessments on all your internal and third-party applications to eradicate the risk of one-time or point-in-time evaluations.

CISOs - Transforming risk assessments | TrustCloud

CISOs struggle with risk assessment. Reduce risk and financial liability with TrustCloud. Take your risk register from manual spreadsheets to programmatic, predictive risk assessments. Monitor and forecast your risks in real time, enable IT risk quantification to prove financial impact to the board, and prevent risk instead of managing it.

CISOs - Eradicating Security questionnaires | TrustCloud

CISOs struggle with security questionnaires. Make security reviews the quickest part of closing a deal with TrustCloud. TrustCloud offers a Trust portal and AI to complete security questionnaires, rolled into one. Don’t let security reviews slow down sales (or take over your life). TrustShare’s secure, public-facing portal invites prospects to view compliance reports and complete security reviews on their own. If there’s a questionnaire, TrustShare pre-fills up to 85%, using information from prior questionnaires and artifacts in your security program.

GRC Engineering for Revenue Acceleration | TrustCloud

How to build a Customer Assurance and Continuous Control Monitoring Program that earns customer trust. Join us for a practical and insightful conversation on how transparent security and compliance posture sharing , high-confidence AI-assisted security questionnaire completion, and continuous control monitoring (CCM) translate directly into customer assurance, revenue acceleration, faster sales cycles, and higher buyer confidence.

Upgrade GRC into a Profit Center and Business Enabler | Strategic CISOs by TrustCloud

A candid, practical session for CISOs and security leaders who need to map security to business priorities and show the ROI of their programs. What you’ll learn: A board-ready strategy that ties security to growth. How to present a four-row “business impact” view that shows contributions to revenue acceleration, product expansion, board protection, and culture, on a single timeline. The first 90 days set you up for the next 3 years. Map to business objectives from day one, educate on the “why”, not just the “what,” and listen so you can pivot with the business.

Third-party risk management: What's next | TrustTalks - Ep 35 | Security and GRC Podcast

Akshay sits down with Paola to discuss Third-party risk management. Third-party risk isn’t just a security checkbox anymore, it’s becoming one of the most dynamic and high-stakes areas of enterprise risk. In this episode, we unpack where third-party risk management is headed: from static spreadsheets to real-time monitoring, from annual audits to AI-driven insights, and from compliance pressure to competitive advantage.