Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cybersecurity Awareness Month: Securing the Next 250 with Cyber Threat Hunting

October has made a strong case for this year’s Cybersecurity Awareness Month (opens in a new tab) theme, “Securing the Next 250,” chosen in honor of the U.S.’s 250th anniversary. The initiative, started by the Cybersecurity and Infrastructure Security Agency (CISA) and the National Cybersecurity Alliance (NCA), occurs annually in October to raise awareness about online safety and empower individuals and businesses to protect themselves from cybercrime.
eMudhra CA Compromise: Find and Fix Your Exposure with Tanium

On October 17, 2026, a researcher reported that eight intermediate certificate authorities (CAs) run by eMudhra have private keys that anyone can calculate from the public certificates. Six of the CAs are for TLS (website) certificates and two are for code signing. Sectigo cross-signed the same eight keys, so 16 certificates are affected in total With these keys, anyone can issue a certificate for any website, or sign software, and it chains to root CAs that many systems trust.

HTTP2Shell: Find and Fix Vulnerable Brotli Copies with Tanium

If you run Node.js, update to 26.12.1, 24.22.1 or 22.23.4 now. If you run Python, upgrade the Brotli package to 1.2.1 and brotlicffi to 1.2.1.0. If you run Bun, move to 1.4.4. All three carry a fix for CVE-2026-111497, an out-of-bounds write in Google's Brotli decoder that can let a remote, unauthenticated attacker crash a process, read its memory or potentially run code by sending it crafted compressed data. Google's CVE record scores it 9.2 under CVSS v4.0.

AI Compute Just Became an Endpoint Problem

For the last three years, enterprise AI happened somewhere else. Models trained in someone’s cloud, inference ran behind an API, and the endpoint stayed where it had always been: on a laptop that opened a browser. With local AI computing platforms like NVIDIA DGX Spark (opens in a new tab), RTX Spark (opens in a new tab), and DGX Station (opens in a new tab), that framework is ending.

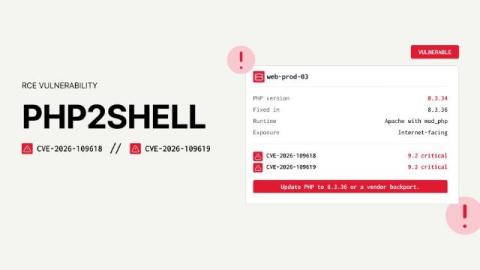
PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619

If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed this week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part.

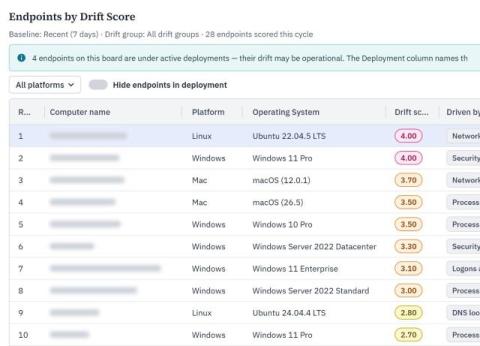
Notice when a machine stops acting like itself: introducing Endpoint Drift

The next attacker in your environment probably won't look like an attacker. With AI in the mix, they can sign in with stolen credentials and use the same tools your IT team uses every day. Nothing about that activity matches a known-bad file or a known-bad rule. That is the problem Endpoint Drift is built to solve. It learns what normal looks like for each endpoint, then shows you which ones have started behaving differently, and why.

Hunt or be Hunted: Every service was unique, and that was the problem

Stacking is usually the first thing we reach for on a persistence hunt. Pull every service, autorun or scheduled task across the environment, count how many endpoints have each one, and sort ascending. The entries at the bottom, the ones that show up on one or two machines, are where you start digging. In one Tanium Customer's environment, that didn't work at all. Each endpoint returned somewhere between a hundred and five hundred rows, and almost every one of them was unique to that endpoint.