Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

ISO 42001 Readiness Checklist: 15 Questions to Ask Before Certification

Getting an AI policy approved is not the same as being ready for ISO/IEC 42001 certification. Your organization may already have risk registers, information security controls, model documentation, supplier assessments and responsible AI principles. The more important question is whether these elements operate together as an Artificial Intelligence Management System (AIMS) — and whether you can demonstrate that with evidence. Before asking: “How quickly can we get ISO 42001 certified?”
NIS2 and GDPR Compliance: How European Companies Can Reduce Duplicate Compliance Efforts

NIS2 and GDPR cannot be merged into one legal obligation, but much of the compliance work behind them can be consolidated. Organisations can use one control framework, shared asset and risk information, common supplier assessments and a single incident record while maintaining separate legal registers and notification workflows. The key is to consolidate evidence and operational processes — not the obligations themselves.

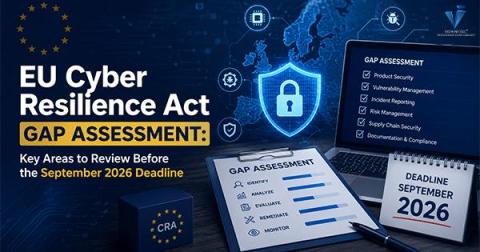
CRA Compliance Gap Assessment: How to Identify Your Compliance Gaps

A CRA compliance gap assessment compares what your organization does with what Regulation (EU) 2024/2847 requires. It reviews each product and each role. It then produces a prioritized list of shortfalls. The list includes named owners, evidence pointers, and dates. It is not a conformity assessment. A conformity assessment decides whether a product may carry the CE marking. A gap assessment tells you whether you would survive one.

AI/LLM Penetration Testing in 2026: The Complete Guide

Most organisations now run at least one LLM in production, and a growing number run agents that call tools and act without a human in the loop. The security testing those systems receive was designed for deterministic software. AI applications fail differently. The payload is natural language, the same input can be safe nine times and unsafe on the tenth, and the malicious instruction often arrives inside a document or tool description rather than from the user.

Cyber Resilience Act Compliance Checklist: 15 Steps to Prepare Before 2027

The EU Cyber Resilience Act makes cybersecurity a condition of market access. A product with digital elements sold in the EU must demonstrate security by design, secure defaults and working vulnerability management — or it does not get a CE mark. This Cyber Resilience Act compliance checklist turns Regulation (EU) 2024/2847 into 15 steps, in execution order.

SOC 2 Type 2 Audit Requirements for Fintech Companies: The Complete Checklist

For fintech companies that move money, store account data, or connect to banking rails, trust must be documented. It cannot just be promised. A SOC 2 Type 2 report is the primary way financial platforms prove their security controls actually work. Demonstrating real fintech security and compliance unlocks enterprise partnerships, closes larger deals, and satisfies vendor security reviews. Banks and payment networks require these reviews before they integrate with you. Free Consultation.

TISAX vs ISO 27001: What German Automotive Suppliers Need to Know

TISAX and ISO 27001 are related but not interchangeable. ISO 27001 is a general-purpose information security certification accepted across any industry; TISAX is the automotive industry’s mandatory, shared assessment framework, built on ISO 27001’s structure but adding prototype protection and data protection requirements that OEMs specifically demand. Most automotive suppliers need TISAX, and an existing ISO 27001 program is the fastest route to get there.

EU CRA Gap Assessment: Are You Ready for 2026?

Most compliance teams have filed the EU Cyber Resilience Act under “2027” — the date the regulation becomes fully applicable. That’s the wrong filing date. From 11 September 2026, manufacturers must already report actively exploited vulnerabilities and severe incidents affecting products with digital elements, more than a year before the rest of the regulation takes effect.

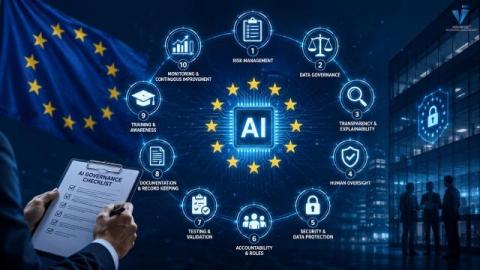
EU AI Act Readiness: 10 Controls Every Organization Should Implement in 2026

This is for compliance and security leaders who already know the EU AI Act applies to them and need a concrete control set for where the law actually stands today — not a summary written before the rules changed. Awareness is done; 2026 is the year of implementation, and the rules just moved. On 29 June 2026 the Council of the EU gave its final green light to the Digital Omnibus on AI — the package that resets several of the dates compliance teams have been building toward.

How Long Does ISO 42001 Certification Actually Take? A Realistic Timeline

ISO 42001 certification usually takes four to twelve months. This runs from the gap assessment to the certificate. For a 50 to 200-person organization, first-year costs are about $85,000 to $150,000. Businesses with an existing ISO 27001 system can often certify in three to four months. This guide is for compliance and AI leaders planning an ISO 42001 project. It gives a realistic timeline and budget, not a vendor’s best-case pitch.