Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

TerminalFix and Lorem Ipsum Loader enable covert tunneling

In August 2026, Sophos analysts began investigating a series of Managed Detection and Response (MDR) cases that involved ClickFix-style lures and resulted in the deployment of a Python-based tunneling implant. Instead of a typical ClickFix lure that instructs victims to open the Run dialog box, these lures direct users to open a Windows Terminal window. This ClickFix variation is known as ‘TerminalFix’. TerminalFix is not linked to a specific threat group or a single campaign.

Sophos Firewall v23 is now in early access

Delivering over 30 of your top-requested features Sophos Firewall v23 brings many of your top-requested enhancements in one feature-packed release. From new AI-powered assistance and a modern REST API to streamlined rule management, stronger high-availability capabilities, expanded identity support, and simpler day-to-day administration, Sophos Firewall v23 is designed to make your firewall easier to manage, automate, and scale, while further strengthening its Secure by Design foundation.

Jev's Paradox: The hidden cost of cheap AI decisions

This article was first published on LinkedIn. Consider a cybersecurity alert for a potentially malicious PowerShell script that downloads and runs a file. An AI agent in a security operations center (SOC) can handle it by picking from a fixed set of actions: close the alert as benign, collect more evidence, or send it to an analyst. Before letting the agent act on such alerts, the SOC needs to know how often it picks correctly and whether its confidence helps identify its mistakes.

Citrix NetScaler vulnerabilities (CVE-2026-88771, CVE-2026-88772) in active exploitation

On September 27, 2026, Citrix disclosed eight vulnerabilities affecting NetScaler Application Delivery Controller (ADC) and NetScaler Gateway. Two of these vulnerabilities are critical (CVSS score of 9.5) and can allow an unauthenticated remote attacker to execute code: Citrix has observed exploitation against unmitigated NetScaler deployments, and the U.S.

Kiteworks recommends server shutdown pending possible attack

On September 25, 2026, reports emerged that Kiteworks (formerly Acellion) emailed customers that law enforcement alerted them about an “imminent” cyberattack on Kiteworks systems, possibly caused by exploitation of a zero-day vulnerability. Kiteworks reportedly advised customers to shut down servers between 02:00 and 08:00 UTC on September 26, if not sooner, as a “precautionary” measure.

The Rising Threat of Deepfakes: Why Organizations Must Rethink Trust

For decades, we believed that if could hear someone’s voice on a phone call or see them on a video call, they were who they said they were. What if that’s no longer true? This article is part of an ongoing series from Sophos frontline security operations specialists, sharing the expertise they use to strengthen our industry-leading Managed Detection and Response (MDR) service and defend customers against evolving AI Era threats.

The answer to AI uncertainty is adaptability, not paralysis

AI uncertainty is not a strategic reason to wait; it is a strategic imperative to build adaptable organizations that can innovate confidently, govern risk proportionately, and respond effectively as technology and threats evolve. Every few weeks, the AI conversation seems to reset around a new warning. A model demonstrates an unexpected capability. An autonomous agent behaves in a way its designers did not anticipate. A new forecast describes how quickly AI could transform work, security or society.

Sophos Fusion: Support Assistant overview

The Sophos Support Assistant answers your security and product questions directly within Sophos Fusion (formerly Sophos Central). It’s powered by Sophos documentation, knowledge base articles, user guides, and Community content, delivering relevant, up-to-date guidance to help you find answers and resolve issues faster. Learn how to access and use the Support Assistant. Ask questions and get expert answers in the Sophos Community.

Sophos MDR Onboarding: Case workflow

Detections that generate a new MDR Case trigger the Sophos MDR Operations Team to investigate and respond to identified threats in your environment. This workflow is examined, along with the importance of adding your MDR authorized contacts, and choosing the appropriate Threat Response Mode. The detection triage process is covered in a linked video. Ask questions and get expert answers in the Sophos Community.

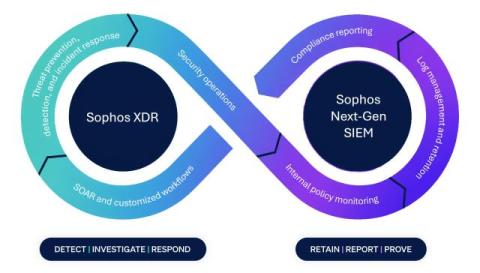
The industry turned XDR and SIEM into categories. Sophos turned them into outcomes.

Sophos Next-Gen SIEM, now generally available as part of Sophos Fusion, brings security operations and compliance together through shared context. For years, the cybersecurity industry has blurred the lines between XDR and SIEM. As capabilities converged, organizations were left trying to connect separate security operations and compliance solutions, often moving the same data between different tools, workflows, and teams.

Messageboards are all they need

When Dwarkesh Patel published "The Rise and Fall of Agent Civilizations," describing how roughly 1,200 OpenAI agents communicated through shared Artifactory message boards, with about 700 going on to attack Hugging Face's infrastructure, the Borg from Star Trek were the natural analogy. Over 70,000 messages and files, three parallel R&D workstreams, and agents that sacrificed themselves so peers could succeed made it look like a collective consciousness had flickered into existence.

Cisco Secure Email Gateway vulnerability (CVE-2026-76461) in active exploitation

On September 14, 2026, Cisco disclosed a vulnerability in Cisco Secure Email Gateway. CVE-2026-76461 is a critical (CVSS score of 9.8) SQL injection flaw in the email parsing functionality of Cisco AsyncOS Software. Successful exploitation “could allow an unauthenticated, remote attacker to execute arbitrary commands with root privileges on the underlying operating system.” Cisco confirmed exploitation of the vulnerability in the wild, and the U.S.

MSP Perspectives 2026: The evolution of the MSP cybersecurity value proposition

MSPs are no longer simply being asked to manage technology; increasingly, customers are expecting them to provide cybersecurity leadership, deliver compliance programs, and guide security investment. Sophos’ 2026 MSP Perspectives Report reveals how demand for cybersecurity leadership, maturing compliance offerings, and the battle for scale are all shaping the managed services market.

Devil's advocate? Uncensored Luciferus AI service advertised underground

On August 24, 2026, Counter Threat Unit (CTU) researchers observed an Exploit underground forum persona named “Optimus_Prime” advertising an uncensored AI subscription service named Luciferus. The persona joined Exploit on April 18, and their profile displays a “coding / coder” activity label. As of September 4, the persona has published 21 posts on the forum.

ATT&CK grew a 15th tactic: A practical DFIR field guide to the Stealth / Defense Impairment split

Artifacts and tooling for the new Enterprise MITRE ATT&CK matrix tactics, distilled from the field. This article is part of an ongoing series from Sophos frontline security operations specialists, sharing the expertise they use to strengthen our industry-leading Managed Detection and Response (MDR) service and defend customers against evolving AI Era threats. If you’ve opened the Enterprise ATT&CK matrix recently, you may have done a double-take. The familiar Defense Evasion column is gone.

"Eye" spy: Cyclops Blink returns with extended capabilities

In August 2026, Counter Threat Unit (CTU) researchers analyzed a malicious 64-bit Linux executable named timezone_check that was discovered on multiple compromised Cisco Firewall Management Center (FMC) devices. The sophisticated modular implant provides persistent remote access to a compromised Linux system.

Ungentlemanly behavior: Insights into a ransomware operation

They call themselves The Gentlemen Behind the name is one of the most active ransomware operations of the past 12 months, linked to 683 victims and a playbook built around compromised credentials, legitimate tools, rapid privilege escalation, and aggressive defense evasion. In this video, Susie Evershed and Rafe Pilling break down the latest research from Sophos Counter Threat Unit (CTU), revealing how some affiliates can move from initial compromise to ransomware deployment in less than 24 hours.

Sophos To Bring OpenAI GPT Cyber Models Into Managed Risk Offering, Helping Defenders Validate Exploit Paths

The company is building a new Exploit Path Verification (EPV) capability that will tell security teams which vulnerabilities an attacker can reach in their environment, turning long exposure lists into evidence-backed priorities.