Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell Didn't Break the Internet (Yet)

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) arrived with predictions of a Log4Shell-scale mass exploitation event. Panic was visible, many rushed to update or even disconnect systems from the Internet until a patch was applied. PHP runs a large share of the web and the vulnerable ranges were reported to cover every branch from 5.4 to 8.5, which are essentially the majority of versions we can see deployed in the internet installed base.
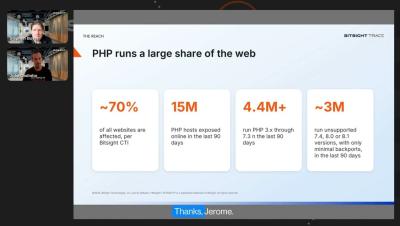
PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

Could PHP2Shell pose a cybersecurity risk on the scale of Log4j? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. With millions of potentially affected systems and limited patching options for legacy PHP versions, security teams face a complex remediation challenge.

Third-Party Cyber Risk: The Regulatory Trends Reshaping Your Program

As U.S. and EU regulators increase scrutiny of third-party cyber risk, organizations face growing pressure to demonstrate effective vendor oversight, continuous monitoring, and risk management. In this Bitsight webinar, Jake Olcott, VP of Government Affairs and former legal counsel to the House Homeland Security Committee and Senate Commerce Committee, explores the regulatory developments shaping third-party risk management (TPRM) heading into 2027.

Introducing Bitsight MCP and AI Mode: Cyber Risk Intelligence Built for the Agentic Era

AI is changing how attackers find and exploit weaknesses, and how security teams respond. As teams bring AI into more of their work, the data and context behind it becomes just as important as the model itself. Today, Bitsight is expanding how customers can use our industry-leading intelligence through three experiences: AI Mode, Bitsight MCP, and Bitsight Skills.

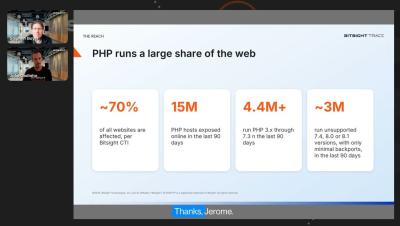
PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

Could PHP2Shell become the next Log4j-scale cybersecurity threat? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. In this webinar, Bitsight cybersecurity experts examine the potential impact of PHP2Shell, share findings from Bitsight's latest exposure research, and explain how security teams can identify vulnerable assets, assess third-party risk, and prioritize remediation.

CVE-2026-109618 and CVE-2026-109619 (PHP2Shell): Two Critical PHP Remote Code Execution Flaws

The PHP security team has announced an emergency security release for Wednesday, October 21, 2026 at 14:00 UTC. It addresses two critical vulnerabilities, both rated CVSS v4.0 9.2. The vulnerabilities are tracked as CVE-2026-109618 and CVE-2026-109619. Both bugs are described as remote code execution issues, meaning an attacker could get their own commands running on a vulnerable server. The route to disclosure was messy.

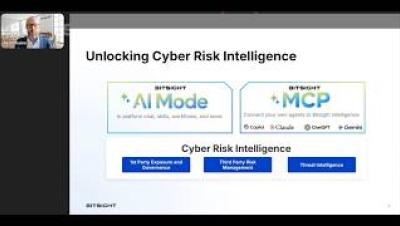
Bitsight MCP and Agentic AI Workflows: A Practical 90-Day Guide

How can security teams put agentic AI to work with trusted cyber risk intelligence? Discover how Bitsight MCP and Bitsight AI Mode help teams investigate cyber exposure, prioritize vulnerabilities, assess third-party risk, and automate security workflows. In this 45-minute webinar, Bitsight experts Christina Chehade and Tadd Hopkins demonstrate practical ways to bring AI into cybersecurity operations, from natural-language investigations to repeatable agentic workflows. You'll also get a 30/60/90-day roadmap for moving from initial exploration to scalable automation.

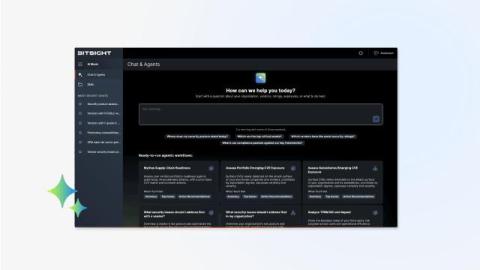
Bitsight AI Mode: AI-Powered Cyber Risk Intelligence & Agentic Workflows

Meet Bitsight AI Mode, a new way to investigate cyber risk, prioritize critical exposures, and accelerate security decisions using AI-powered intelligence and agentic workflows. Built directly into the Bitsight platform, AI Mode combines conversational AI with automated, multi-step analysis to help security and risk teams turn complex cyber risk data into actionable insights. With Bitsight AI Mode, you can.

The New Frontier of Malicious AI: What Underground Forums Tell Us About the Evolution of Cybercrime Tradecraft

Public discussion of AI-enabled cybercrime tends to lean heavily on vendor marketing and speculation about future capabilities. We wanted to measure what criminal practitioners are actually discussing, what tools they prefer, and where their attention is shifting.

DragonForce Ransomware Profile: From Affiliate Program to Cybercrime Cartel

When people discuss DragonForce, two distinct names usually come up: DragonForce Ransomware and DragonForce Malaysia. To set the record straight, the ransomware operation isn't necessarily the same entity as DragonForce Malaysia. DragonForce Malaysia operates as a politically driven hacktivist collective known for pro-Palestinian campaigns, defacing websites, launching DDoS attacks, and leaking data.

Power Grid Attacks Aren't New. So Why Are They So Electric Right Now?

In late July 2026, 36 municipal waste and water systems across Minnesota were targeted in a cyber attack. The attackers targeted Programmable Logic Controllers (PLCs) that were in control of pressure, pumps, and chemical dosing. When the news broke, it felt like it was everywhere. This was an attack on critical systems, systems that we require and use daily. But cyberattacks on U.S. critical infrastructure systems like water, hospitals, sewage, gas, and electricity aren’t new.

Frontier AI Impact Series, Part 2: How Attackers Choose Their Door | Bitsight

How much attention are you giving the doors outside your own network? Your security team may be watching a high-profile CVE closely. An attacker might be looking at a stolen session, a phishing kit, or a supplier with slower response times. Frontier AI gives them more ways to explore those routes. Bitsight’s Emma Stevens breaks down that decision in part two of our video series.

Frontier AI Impact Series, Part 1: Why Attackers Stopped Waiting for Zero-Days | Bitsight

Frontier AI can shrink weeks of vulnerability research into exploitation in hours. What does that mean for the flaws your team deprioritized years ago? Bitsight’s Emma Stevens, Senior Threat Intelligence Advisor, breaks it down in the first video of our new series.

The Attribution Trap: What Happens When Threat Actors Manipulate the Story of an Attack?

Imagine waking up Monday morning to discover you’ve been breached. The attacker has stolen sensitive financial data, set up persistent access, and then greets you with a lovely ransom note at 8:00 a.m. demanding money in exchange for the encryption key. Immediately, you reach out to your security operations team, and they quickly begin assessing the damage and reviewing the breadcrumbs left behind.