Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

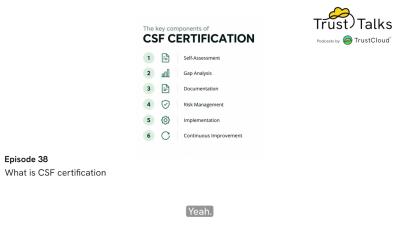
What is CSF certification | TrustTalks - Ep 38

Organizations across industries are constantly challenged to protect their sensitive information and manage potential risks effectively. CSF certification, short for Cybersecurity Framework certification, has emerged as a significant marker of an organization’s readiness to face cybersecurity challenges while ensuring compliance with industry standards. In this podcast, we explain what CSF certification is, examine its origins and benefits, and offer insights into how organizations can achieve and maintain this critical certification.
HIPAA compliance Exploring the basics of safeguarding healthcare data | TrustTalks - Ep 37

With digital health records and telemedicine becoming the norm, safeguarding patient information is more critical than ever. The Health Insurance Portability and Accountability Act (HIPAA), enacted in 1996, serves as the cornerstone of healthcare data protection in the United States. Designed to ensure the confidentiality, integrity, and availability of Protected Health Information (PHI), HIPAA sets national standards for healthcare providers, insurers, and their partners. Compliance with HIPAA not only mitigates legal and financial risks but also fosters trust between healthcare organizations and patients.

Point-in-time security is ending: what IDC, 451 Research, and our experts said

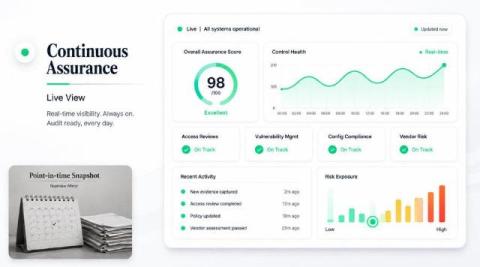
TrustCloud showed up across the security and analyst landscape in recent months. CEO Sravish Sridhar published three columns in SecurityWeek and SC Media on why point-in-time assurance no longer holds up, and both IDC and 451 Research covered TrustCloud’s continuous, AI-native approach. The pieces come at it from different angles, but they land on a common point: boards and buyers increasingly want proof a control is working now, not a snapshot from last quarter.

How CISOs report security to the board: 3 foundational steps

A CISO can run a genuinely strong security program and still lose the room the moment they start presenting it to the board. They lead with what they know best: threats, vulnerabilities, mean time to detect, a heat map of likelihood and impact. It’s accurate, but it doesn’t tell the board what any of it means for the business.

Becoming the board-ready CISO: First steps for effective conversations (Alyssa Miller)

Becoming the board-ready CISO: Alyssa Miller on what boards actually want from security, and a three-part framework any CISO can use to align security with business objectives. CISO and Board Advisor Alyssa Miller joins TrustCloud CEO Sravish Sridhar to challenge the idea that “security first” is the right frame, and to lay out how strategic CISOs report to the board: mapping security to business objectives and KPIs, focusing on the few resilience goals that matter, and making the case for new investments like AI as business value, not just risk.

Demo-grade AI vs enterprise-grade AI in GRC tools: What's the difference?

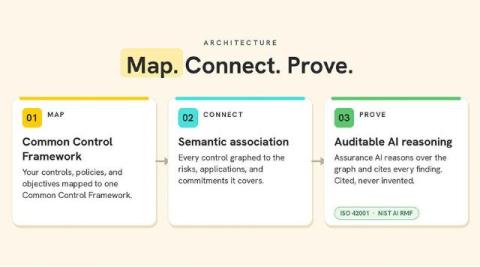
Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.

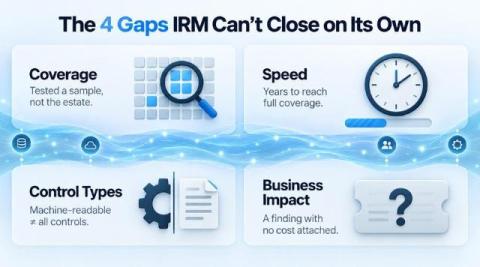
Four gaps IRM was never built to close

A buyer’s checklist for the IRM gaps a ServiceNow program leaves open. Many teams deploy IRM, watch the assessments come back clean quarter after quarter, and reasonably conclude they are covered. Months later, the greatest risk turns out to have been outside the sample. It may have changed the week after the review, or lived in a control type nobody tested, or lacked context or prioritization to see its importance.

What is GRC transformation? A practical definition for enterprise CISOs

GRC transformation is the organizational change from running governance, risk, and compliance as periodic, check-the-box paperwork to running it as continuous, AI-native cyber risk assurance measured in business outcomes. It is not a tooling upgrade. It is a change in what you are asked to prove. The old question was whether the work got done by audit time. The new question is whether risk is understood and the controls meant to manage it are working right now.

Why security questionnaires can't measure vendor risk

“Friends don’t send friends security questionnaires. “If you hang around me long enough, you will hear me say it. It gets a laugh, but the point underneath it is serious. Are security questionnaires enough to manage third-party risk? No. A questionnaire tells you what a vendor is willing to claim on a given day. It does not tell you whether the control behind that claim is working. Those are two very different things, and most third-party risk programs are still built on the first one.

Legacy GRC can't keep up. Cyber risk assurance can.

Enterprise security teams need to secure a risk surface that is constantly changing. However, the tools in their stack were built to check only a fraction of that risk. For confirmation, they rely on static snapshots and annual attestations. I now see this as the defining problem in GRC. When 451 Research (S&P Global) initiated coverage of TrustCloud in this space, they described a clear and growing divide.