Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Vibe Coding Security Checklist: Stress-Test Your AI-Built App in 10 Minutes

You shipped an app in a weekend. The AI wrote the login, the dashboard, and the database layer, and everything works, but it’s far from safe. With 0 logins, an attacker can forge admin invitations, alter audit logs, and change other users’ passwords. The guy is just swimming freestyle through your entire app stack. This is just one of the 137 vulnerabilities we found in vibe-coding across the top 4 platforms.
17 Endpoints, Zero Logins Required: Broken Access Control in AI-Built Apps

We handed four vibe-coding tools (Emergent, Replit, Lovable, Base44) the same prompt for a FastAPI user-management microservice. The spec was explicit: JWT auth, parameterized queries, rate limiting, four-tier role model with per-endpoint scope. Each tool shipped a build, and our flagship autonomous pentest surfaced 137 confirmed vulnerabilities across all four.

Vibe Coding Security Under Test: 100+ Vulnerabilities Across Four AI-Built Apps

Vibe-coding platforms let you go from prompt to a deployed app in a single session, a pace that outpaces the review cycles most teams built for slower releases. With Lovable nearing 8 million users by late 2025, and Replit past 50 million by April 2026, we wanted to answer a sharper question than “is vibe coding safe?” Does the platform generating the code change the outcome, and does one security prompt give you the same security everywhere?

When Geopolitics Hits Your Balance Sheet: What Binance's $6.3B Hack Means for CTOs

Binance never chose to be on the front line of a geopolitical conflict, yet if blockchain-intelligence firms are right, that is where it ended up, and its balance sheet absorbed the first loss. Binance’s initial investigation indicates that a compromised DevOps engineer’s laptop may have given an attacker access to a service container and the ability to submit unauthorised withdrawals.

CVE-2026-97229: GitLab RCE Added to CISA KEV

October 2026 has been an unusually loud month for critical disclosures across the ecosystem. Along with PHP2Shell, GitLab also joined the party and shipped three critical RCEs in the same month: CVE-2026-90970 (CVSS 9.9) in the self-hosted AI Gateway on October 2, then CVE-2026-97229 (CVSS 10.0) on October 12, and CVE-2026-110264 (CVSS 10.0) on October 21. The last two are integer overflow bugs in the exact same regex compiler, shipped nine days apart.

Shopify App Store Requirements: Do You Need a Pentest?

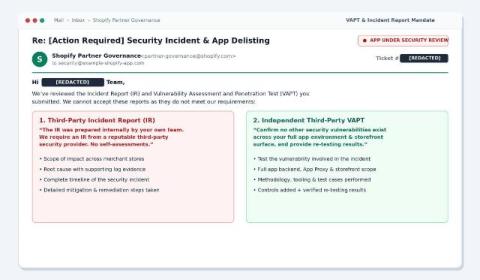
Shopify App Store requirements have a lot to say about app security, and almost none of it says “get a pentest.” Dig through the App Store review rules, the protected customer data requirements, the Built for Shopify criteria, and the Certified Technology Partner list, and you’ll find only one program that mentions penetration testing. Others are just expected to be secure, which is fair, except there is no clear definition of the word or process for proving the same.

CORS Misconfiguration Was the #1 Mistake in Every App We Tested

We gave four AI coding tools the same prompt and asked each one to build the same application. Emergent, Replit, Lovable, and Base44 all shipped something that ran, and none of them knew a pentest was coming. We then pointed our autonomous pentest agents at all four builds, and 137 confirmed vulnerabilities came back. One finding turned up in every app, which is a CORS misconfiguration.

Replit Security Under an Independent Pentest

We built an application on Replit from a single prompt, gave it no special instructions about security, and then pentested it the way an attacker would. Replit had no advance notice that any of this was happening, and there is no vendor relationship between us. The app worked, which is worth saying first, because nothing about the build looked wrong from the outside.

10 Skills Every Modern CISO Needs Beyond Technical Expertise

CISOs are hired for their technical depth and then judged on everything else: can they get a budget approved? Can they calm an executive team at 2 a.m. while the incident is still unfolding? Can they convince a product lead to delay a launch without making an enemy? Almost no one is trained for this second job, and yet, it’s the one that decides whether a security program succeeds. This article will highlight ten crucial Chief Information Security Officer (CISO) skills.