Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Insider Threats including employee monitoring and data privacy.

The Pretext: Insider Threats

Cybercriminals are looking for a few good... actually, bad... insiders. Malicious insiders enact revenge for termination or line their pockets with ill-gotten funds through partnership with threat actors, giving up their credentials, stealing data, or agreeing to install malware on their organization's environment. How to prevent them? Watch this session from Arctic Wolf® Managed Security Awareness!
The Hidden Danger - Understanding and Defending Against Insider Threats

Cyber threats do not always come from outside an organization. Insiders, including current and former employees, contractors and other business partners with authorized access to your network, systems or data can pose significant risk, damage your reputation or even cause financial losses and business disruption. Insider threat incidents are on the rise and organizations affected by them spend on average $15.4 million on mitigation efforts.

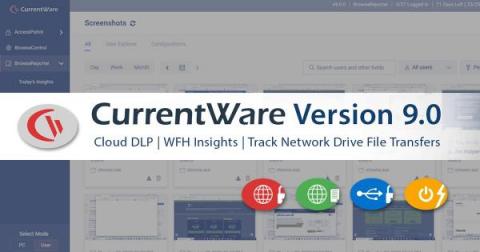
New DLP Tools, Location Insights, Track Network Drives, and More! (v9.0) | CurrentWare

CurrentWare version 9.0 is here! This update introduces transparent packet filtering technology, allowing for significant enhancements to the tracking and restriction capabilities of the CurrentWare Suite. By upgrading to CurrentWare v9.0 you will have greater protection against the data security risks of cloud storage services, potentially malicious file downloads, network share drives, and more!

Major Supply Chain Cybersecurity Concerns and 7 Best Practices to Address Them

In today’s complex and interdependent world, it’s incredibly difficult to deliver a product or service without a supply chain. But this dependency creates additional risks – from reputational losses to major business disruptions. And with 62% of organizations being impacted by supply chain cyberattacks in 2021, mitigating risks created by third parties is extremely important.

Work From Home, Quiet Quitting, and How Insider Risk Has Changed

March 2023 marks approximately three years since the world shut down at the beginning of the Covid-19 pandemic. Since then, organizations have seen their workforce change considerably. What was originally a short term plan to work from home has become ingrained in our new work culture. According to a recent LinkedIn poll, at-home work is ticking back up. Only 50% of workers are in the office full-time, the rest work from home full-time or have a hybrid schedule.

Data Loss Prevention (DLP) Systems: Types, Key Features, Pros and Cons

As the number and severity of cybersecurity attacks rise each year, organizations are compelled to look for measures to protect sensitive data. The abundance of cybersecurity solutions on the market may create confusion and pressure, as choosing the wrong one may lead to security gaps. Many companies turn to data loss prevention (DLP) systems, since they have been on the market for years. But is a DLP system enough to protect your data?

New DLP Tools, Location Insights, Track Network Drives, and More! (v9.0)

CurrentWare version 9.0 is here! This update introduces Advanced HTTPS transparent packet filtering technology, allowing for significant enhancements to the tracking and restriction capabilities of the CurrentWare Suite. By upgrading to CurrentWare v9.0 you will have greater protection against the data security risks of cloud storage services, potentially malicious file downloads, network share drives, and more!

How to Effectively Communicate IT Security to the Executive Board: 7 Best Practices

Regular communication with CISOs may not be enough for the board to fully understand and adequately invest in cybersecurity. According to a survey conducted by Neustar International Security Council in November 2022, only 49% of organizations have the requisite budget to meet their cybersecurity needs. Thus, only half of all CISOs receive enough resources to enforce effective cybersecurity strategies.