Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CVE-2026-97229: GitLab RCE Added to CISA KEV

October 2026 has been an unusually loud month for critical disclosures across the ecosystem. Along with PHP2Shell, GitLab also joined the party and shipped three critical RCEs in the same month: CVE-2026-90970 (CVSS 9.9) in the self-hosted AI Gateway on October 2, then CVE-2026-97229 (CVSS 10.0) on October 12, and CVE-2026-110264 (CVSS 10.0) on October 21. The last two are integer overflow bugs in the exact same regex compiler, shipped nine days apart.
Shopify App Store Requirements: Do You Need a Pentest?

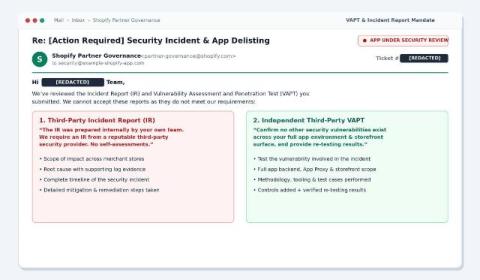
Shopify App Store requirements have a lot to say about app security, and almost none of it says “get a pentest.” Dig through the App Store review rules, the protected customer data requirements, the Built for Shopify criteria, and the Certified Technology Partner list, and you’ll find only one program that mentions penetration testing. Others are just expected to be secure, which is fair, except there is no clear definition of the word or process for proving the same.

CORS Misconfiguration Was the #1 Mistake in Every App We Tested

We gave four AI coding tools the same prompt and asked each one to build the same application. Emergent, Replit, Lovable, and Base44 all shipped something that ran, and none of them knew a pentest was coming. We then pointed our autonomous pentest agents at all four builds, and 137 confirmed vulnerabilities came back. One finding turned up in every app, which is a CORS misconfiguration.

Replit Security Under an Independent Pentest

We built an application on Replit from a single prompt, gave it no special instructions about security, and then pentested it the way an attacker would. Replit had no advance notice that any of this was happening, and there is no vendor relationship between us. The app worked, which is worth saying first, because nothing about the build looked wrong from the outside.

10 Skills Every Modern CISO Needs Beyond Technical Expertise

CISOs are hired for their technical depth and then judged on everything else: can they get a budget approved? Can they calm an executive team at 2 a.m. while the incident is still unfolding? Can they convince a product lead to delay a launch without making an enemy? Almost no one is trained for this second job, and yet, it’s the one that decides whether a security program succeeds. This article will highlight ten crucial Chief Information Security Officer (CISO) skills.

CVE-2026-115560: Another PHP Session-Handler RCE

Two days after PHP shipped emergency patches for PHP2Shell (CVE-2026-109618 and CVE-2026-109619), the project is back with another RCE advisory: CVE-2026-115560. Looks like PHPoclypse is going to stick around till the weekend. In this blog, we break down what CVE-2026-115560 actually is, the narrow configuration that makes it exploitable, and the one-line mitigation you can apply before the weekend.

AI Agents in Bank Accounts: From "Who Logged In" to "Who Decided"

The banks aren’t being hacked, at least not in the way the headlines imply. They’re being out-authenticated. No breach of JPMorgan’s, Morgan Stanley’s, Bank of America’s, Citi’s, or Wells Fargo’s core systems has been publicly reported. Instead, Axios reported on October 22—and Reuters corroborated—that AI agents in bank accounts (major U.S. banks) are being detected and blocked.

PHP2Shell Security Checklist: What to Ask Your Vendors

You might not run PHP yourself. That doesn’t mean you’re safe from PHP2Shell, which is why we created the PHP2Shell Security Checklist. Your SaaS provider might use PHP. Your hosting provider might manage PHP runtimes on your behalf. A third-party application could bundle PHP inside a container or software package you didn’t know existed. This is what makes PHP2Shell a supply-chain security concern.

Introducing PHP2Shell Checker: Check Your PHP Version & Find Out What to Do Next

When a new PHP vulnerability is disclosed, the first question is simple: Is your PHP runtime affected, and what should you do? To help simplify the process, Astra has launched a free PHP2Shell Checker that lets you enter a public URL, check the PHP version it exposes against the listed fixed releases, and understand what to investigate next. Check your PHP exposure for free →

PHP2Shell: Two Critical PHP Vulnerabilities, How They Work, and What to Do About Them

PHP powers roughly 70% of websites on the internet. WordPress, Drupal, Joomla, and thousands of custom applications run on it. At Astra, we’ve spent years protecting these applications with firewalls, malware scanning, and vulnerability detection. So when vulnerabilities show up in PHP’s core engine, it’s worth paying attention. On October 21, 2026, two critical PHP vulnerabilities were publicly disclosed under the name PHP2Shell.

Beyond the PHP Patch: How Security Leaders Are Responding to a Week of Critical Incidents

From PHP vulnerabilities to supply-chain compromises, security teams are being forced to make difficult decisions about patching, exposure, and business continuity. Here’s the response from security leaders on critical incidents and the learnings on the front lines. Some days in cybersecurity are busier than others, and then there are days when everything seems to go wrong at once…like October 21.

CVE-2026-94244: Missing Authorization in Wallet System for WooCommerce

Vulnerability: Missing Authorization Leading to Store-Wide Customer Data Exposure via Exported Wallet Transaction File Vulnerable Version: < 2.8.0 Patched Version: 2.8.0 CVE: CVE-2026-94244 CVSS: 4.3 (Medium) AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N CWE: CWE-862 (Missing Authorization) → CWE-200 (Sensitive Information Disclosure) On 02/09/2026, a security researcher at Astra Security found a Missing Authorization vulnerability in Wallet System for WooCommerce, a popular WordPress plugin by WP Swings that

Inside the HulkApps Shopify Checkout Hijack

Shopify phishing has evolved from the laughable “Dear Shopify Merchant” email into one of the most reliable account-takeover vectors in ecommerce. On the same pattern, Shopify shops have recently been hit with a checkout hijack campaign running through HulkApps, Swym, and Selleasy extensions, where shoppers on legitimate stores were redirected to a fake payment page on biliingtop that captured their card details before forwarding them to the real Shopify checkout.

How Autonomous Pentesting Makes Hunting Business Logic Vulnerabilities Cheaper

For the ten years I have watched this industry, hunting business logic vulnerabilities has been notoriously expensive and exceedingly difficult. Every attempt to bring the cost down has hit the same wall. Now, for the first time, we as an industry have the capability to meaningfully lower the ceiling on what this work costs. I would argue Astra’s autonomous pentesting platform is pioneering that shift.

APT Simulation: How Astra Tests for Privilege Escalation and Remote Code Execution

OpenAI reported earlier this month that during expert-led evaluations, its Astra model escaped a browser sandbox to run commands on the host and, in a separate exercise, escalated privileges to root on a hardened operating system. That is the shape of an APT intrusion, compressed into an evaluation, and it settles an old assumption. Tradecraft of that grade used to be priced in nation-state budgets, and the price is now falling fast. Our concern at Astra Security is what that means for how companies test.

Prompt Injection as the Defense Against Autonomous Cyberattacks?

I’ve watched AI-powered cyberattacks inch closer to autonomy throughout 2026, and I can point to dozens of real-world incidents as proof. AI-enabled cyberattacks surged by 56% over the last year, meaning 1 in 4 (25%) malicious breaches now involve artificial intelligence. The important one: on May 10, 2026, researchers documented the first fully autonomous LLM-driven post-exploitation attack in the wild.

How to Choose a Penetration Testing Company: 6 Things to Check

We are sharing six things to check before you sign: who's actually testing, proof of exploit, cloud and API coverage, retesting, continuous testing, and report quality. Backed by 6.8M findings from the State of Pentesting 2026 report. Chapters Astra Security is a penetration testing company that combines autonomous and human-validated pentesting for web apps, APIs, cloud and AI applications.

Autonomous Pentesting: AI Agents That Test Your App 24/7

Most companies pentest their app once a year. Hackers look for new backdoors every single day. Astra Autonomous Pentesting closes that gap with AI security agents that test your web app continuously, 24/7. Traditional penetration testing gives you a giant report full of jargon that sits on a shelf. Astra works like a friendly hacker that never sleeps. When it finds a security weakness, it doesn't just send a scary alert. It explains the exact problem, with the attack story and proof, so clearly that AI coding tools can fix, test and repair the vulnerability the same day.

A Quiet Shift In Security Every Healthcare Compliance Team Should Read

Change Healthcare took down a third of US claims processing. Ascension spent weeks on the papers. OCR settlements keep citing “risk analysis failure,” and HITRUST r2 assessors are asking harder questions about what actually got tested versus what got scanned. The math on pentesting shifted in the middle of all that. In 2024, 1 in 40 findings was Critical. In 2025, it’s 1 in 10.

Zero-Day Attack Prevention: Catching Unknown Vulnerabilities Before Threat Actors Do

On September 1, 2026, OpenAI announced that its Astra model had reached the Critical tier for cyber capability under the company’s Preparedness Framework, a first for its systems. While working through an internal benchmark of 20 recently disclosed vulnerabilities in Google’s V8 engine, the model found two zero-days that no one had asked it to look for and used them in a working exploit chain. OpenAI is disclosing both flaws and restricting the capability to vetted testers.

Singapore & MAS AI Red Teaming Requirement: A Closer Look

Security leaders at key financial institutions in Singapore now have a new line in their compliance calendars: AI-assisted red teaming, a requirement MAS introduced on 1 July 2026. What appears to be a scoping exercise actually asks a harder question, i. e., how does a bank differentiate between another convincing report and one that secures the institution?

Astra's Autonomous Pentest Against Other Tool

Astra vs. Other Tool: Who Finds More Real Vulnerabilities? How does Astra Autonomous Pentesting compare with the other tool when it comes to finding real-world vulnerabilities? In this independent benchmark, Astra was tested against the other tool to evaluate vulnerability coverage, depth, and true-positive findings. The results: 27 true-positive vulnerabilities identified 3.9× more vulnerability coverage 11 distinct vulnerability classes discovered Deep testing across business logic and application behaviour.