Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Active-Active Replication: When It's Worth the Complexity

TL;DR: Active-active replication lets every node in a cluster accept writes and sync changes to its peers, which keeps writes available during regional outages but adds conflict resolution, replication lag, higher costs, and no protection against corruption or ransomware. It justifies that complexity mainly for five-nines, multi-region, or edge workloads, while read replicas, sharding, or active-passive setups suit most other needs.
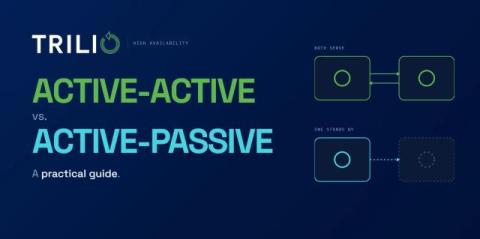
Active-Active vs. Active-Passive: A Practical Guide

TL;DR: Active-active runs every node live so traffic distributes across the pool and failover is near-instant, but it forces you to solve multi-writer conflicts through last-writer-wins, vector clocks, CRDTs, or consensus protocols. Active-passive keeps one authoritative primary with an idle standby, trading seconds to minutes of promotion time for predictable behavior, simpler troubleshooting, and lower cost under steady load.

OpenShift Console: A Practical Guide

Your first login to a Red Hat OpenShift cluster can feel like sitting in an unfamiliar cockpit: dozens of menus, two perspectives, and dashboards full of metrics you haven’t learned to read yet. The OpenShift Console pulls all of it into one browser-based interface, so you can see what’s running, fix what’s broken, and deploy what’s next without memorizing a single oc flag command.

Red Hat OpenShift on IBM Cloud: What It Is and What's New

Running Kubernetes in production takes real work. Patching control planes, managing upgrades, and keeping clusters highly available pulls engineers away from shipping applications. Red Hat OpenShift on IBM Cloud removes that operational load. IBM runs the platform as a fully managed service, and your team keeps its attention on workloads.

Offsite Disaster Recovery: Benefits and Solutions

Most teams find the holes in their recovery plans at the worst possible time: a flooded data center, failed storage array, or ransomware note sitting on the same server as the backup catalog. Offsite disaster recovery removes that single point of failure, but only when the copy is truly separated from production by geography, network path, and access control. Distance by itself won’t save you.

How to Protect Backups from Ransomware

Ransomware crews go after backups first. Before any production file gets encrypted, they hunt down your backup catalog, snapshots, and repository credentials. The real question is whether your backups can survive an attacker who is actively trying to destroy them. This guide covers how to protect backups from ransomware with specifics: immutable and WORM storage, the 3-2-1-1-0 rule, air-gapping, network segmentation, encryption, and access controls that hold up under pressure.

OpenStack Backup And Recovery Frequently Asked Questions

My name is Kevin Jackson. I have been working with OpenStack since the first releases in various capacities — as an operator, author, architect, and currently at Trilio, where I assist organisations with cloud backup and recovery strategies. Over the years, I have watched OpenStack mature from an early-stage project into the core infrastructure underpinning demanding private and public clouds across telecoms, financial services, and the public sector.

Kubernetes Zero Trust: Principles and How to Apply Them

Kubernetes trusts everything inside the cluster by default. Any pod can reach any other pod, IPs change with every rolling deployment, and one compromised container gives an attacker a path across your entire environment. Kubernetes zero trust replaces that default with a simple rule: Never trust, always verify, regardless of where a request comes from.

Digital Sovereignty: What It Is and Why It Matters

Who actually controls your data, your infrastructure, and the software your organization runs on? That question is on the agenda of every CIO and DevOps lead. Digital sovereignty has become a strategic priority, but what does it look like in practice? And why should IT teams care beyond the policy headlines?