

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

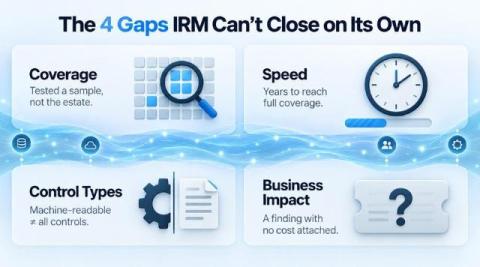
Four gaps IRM was never built to close

A buyer’s checklist for the IRM gaps a ServiceNow program leaves open. Many teams deploy IRM, watch the assessments come back clean quarter after quarter, and reasonably conclude they are covered. Months later, the greatest risk turns out to have been outside the sample. It may have changed the week after the review, or lived in a control type nobody tested, or lacked context or prioritization to see its importance.
What is GRC transformation? A practical definition for enterprise CISOs

GRC transformation is the organizational change from running governance, risk, and compliance as periodic, check-the-box paperwork to running it as continuous, AI-native cyber risk assurance measured in business outcomes. It is not a tooling upgrade. It is a change in what you are asked to prove. The old question was whether the work got done by audit time. The new question is whether risk is understood and the controls meant to manage it are working right now.

Why security questionnaires can't measure vendor risk

“Friends don’t send friends security questionnaires. “If you hang around me long enough, you will hear me say it. It gets a laugh, but the point underneath it is serious. Are security questionnaires enough to manage third-party risk? No. A questionnaire tells you what a vendor is willing to claim on a given day. It does not tell you whether the control behind that claim is working. Those are two very different things, and most third-party risk programs are still built on the first one.