Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CVE-2026-67401: SQL Injection in cPanel's EmailTrack Puts Shared Hosting Environments at Risk

A critical SQL injection vulnerability has been identified in cPanel & WHM’s EmailTrack functionality. The vulnerability was disclosed by cPanel on September 8, 2026, affecting every supported release line. It allows an authenticated cPanel account holder with mail related privileges to ultimately achieve root-level code execution on the underlying host.
AppTrana Adds Post-Quantum Cryptography Support with X25519MLKEM768

Quantum computers could very soon undermine the public-key cryptography that secures financial transactions, health records, and other sensitive data moving over TLS today. When that happens, encrypted information protected by vulnerable cryptography could become accessible. Encrypted traffic can be intercepted and stored today, with the expectation that it will be decrypted once a sufficiently capable quantum computer exists.

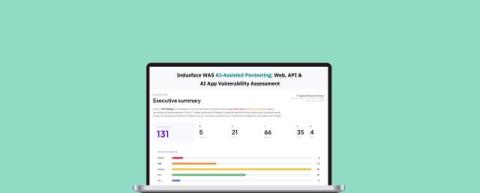
Indusface WAS AI-Assisted Pentest: Comprehensive Vulnerability Assessment Across Web, API and AI Apps

For years, our security team has run pentests against business-critical applications across industries, and one pattern stands out. The vulnerabilities that are the most difficult to remediate are business logic vulnerabilities: IDOR, broken access control, privilege escalation, and multi-step workflow abuse. These are the kind of vulnerabilities pentest experts find by noticing a broken assumption behind one API call and chasing it until the full exploit path becomes clear.

CVE-2026-0768: Critical RCE in Langflow AI Agent Builder

A critical remote code execution vulnerability has been identified in Langflow. The vulnerability was first reported to the vendor in mid-2025 and disclosed publicly as a zero-day in January 2026. Exploitation attempts rose sharply in late August 2026, moving from isolated probing to continuous, multi-source scanning within days.