

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Enforce custom rules in Datadog IaC Security scanning

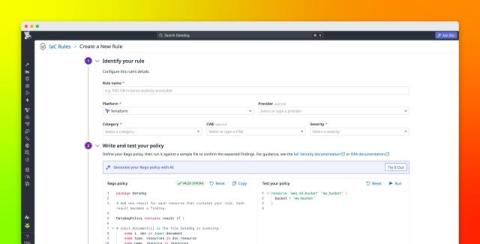
Infrastructure-as-code (IaC) security scanning can catch common misconfigurations before deployment, but every organization also has internal requirements that a default rule catalog cannot cover. For example, teams may need to enforce required tags, approved instance types, or naming conventions. With custom rules for Datadog IaC Security, security and platform teams can define these requirements as Rego policies and run them alongside Datadog’s default rules during IaC scans.
Transform and route security logs to Microsoft Sentinel tables using Observability Pipelines

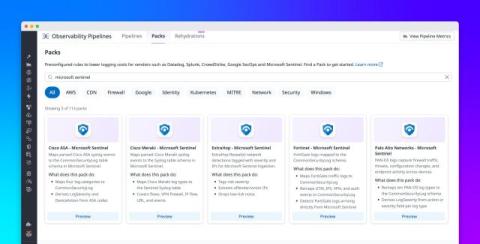
Microsoft Sentinel is Microsoft’s cloud-native SIEM for detecting, investigating, and responding to threats across your environment. To query security data and run analytics rules, Sentinel expects telemetry data in specific table schemas. But firewall, VPN, and network detection logs arrive in vendor-specific formats, making source-specific mappings difficult to maintain as environments grow.

Stop runtime threats with Workload Protection response actions

Modern threats increasingly unfold at runtime, where attackers exploit live workloads, spawn malicious processes, and move laterally across your environment. Detecting that activity is essential, but a signal only matters if you can stop it. When a threat appears, every step before a response gives an attacker more time to act. Datadog Workload Protection can now directly remediate threats with both automated and manual response.